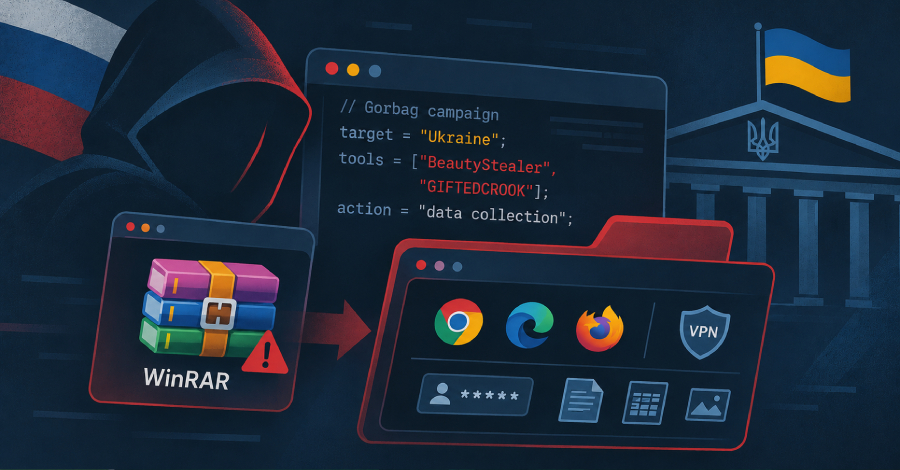
A Russia-aligned threat actor known as Gorbag has been observed using simple information stealer malware in attacks targeting Ukrainian organizations.
"Active since at least February 2025, the group has focused exclusively on Ukrainian targets, with a clear preference for law enforcement and justice entities, local administrations near the front line, and the defense sector," ESET researcher Damien Schaeffer said in a report shared with The Hacker News.
The activity shares overlaps with a cluster tracked by the Computer Emergency Response Team of Ukraine (CERT-UA) under the moniker UAC-0226 and by Trend Micro as SHADOW-EARTH-066. Gorbag is known to be active since at least February 2025.
A key tool in the threat actor's malware arsenal is GIFTEDCROOK, a C/C++ stealer that facilitates the theft of sensitive data from web browsers like Google Chrome, Microsoft Edge, and Mozilla Firefox, such as cookies, browsing history, and authentication data.
Earlier this June, Trend Micro also attributed the adversary to attacks weaponizing a now-patched vulnerability in WinRAR (CVE-2025-8088) to trigger a DLL sideloading chain responsible for executing GIFTEDCROOK.
Stealer malware deployed by Gorbag is also equipped to harvest VPN configurations and documents of interest, raising the possibility that it may be acting as an initial access broker that hands off stolen data to other threat actors, who then can conduct post-exploitation activity of their own.
"If so, Gorbag may represent only the first stage of a longer intrusion chain whose later stages remain to be observed," ESET said.
Source link