Your team is remediating more vulnerabilities than ever, yet your breach risk has barely changed. You’re spending too much time and effort on exposures attackers may never exploit, while higher-risk exposures sit, waiting in the queue. Gartner®’s report on exposure prioritization states that fewer than 10% of vulnerabilities are exploited, yet most are treated as urgent. The report also argues that CVSS scores alone do not predict actual exploitation or business impact.
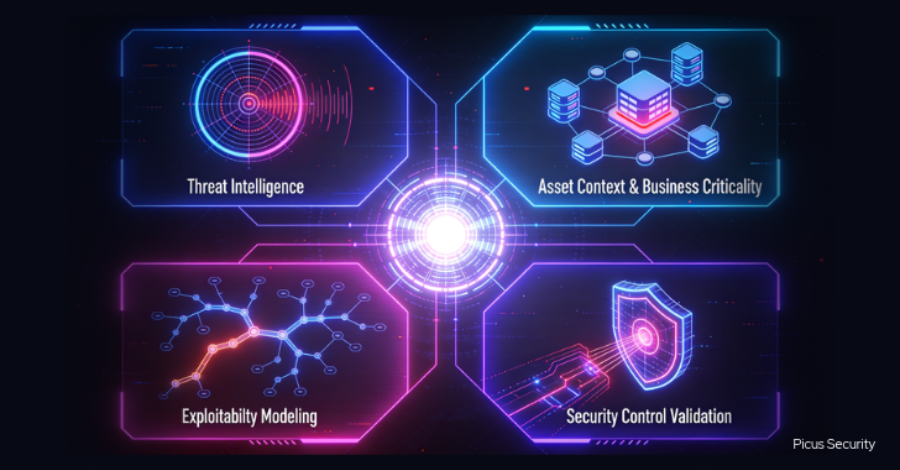
Gartner predicts that by 2028, organizations that prioritize exposures using threat intelligence, asset context, exploitability modeling, and security control validation will reduce breach likelihood by at least 70% compared to their peers relying primarily on CVSS-based vulnerability prioritization. Let’s break down how each element works, and how the Picus Platform puts all four into practice.
Severity-driven prioritization was an entirely rational response for the era it was built in: a static attack surface, scarce adversary tooling, and remediation capacity that exceeded disclosure volume. Suddenly, that world is gone. Enterprises face tens of thousands of new vulnerabilities a year across cloud, SaaS, identity, and supply chain modalities, and AI has compressed time-to-exploit from weeks or months to hours.
Gartner is candid about why teams still anchor on severity, and it’s not a lack of awareness. In fact:
The result is widespread prioritization paralysis, with significant resources being funneled into remediation activity, but with remarkably little measurable risk reduction to show for it.
The smarter path is performing risk-based vulnerability management in its truest sense: measuring success by the exploitable exposures you’ve reduced, not the hypothetical vulnerabilities you’ve closed.
Source link