Google on Monday warned that threat actors are hijacking enterprise access to Large Language Models (LLMs) to fraudulently leverage expensive computing resources and AI services.
The tactic is called LLMjacking, a form of resource hijacking adapted for the LLM era, where an attacker obtains an API key through phishing, source code leaks, misconfigured environments, or exposed client-side code to gain unauthorized access to an organization's LLM accounts, while the legitimate owner covers the consumption costs.
Such attacks have a wide geographical footprint, with impacted entities located in North America, South America, and Asia Pacific across the financial services, retail, technology, and transportation sectors.
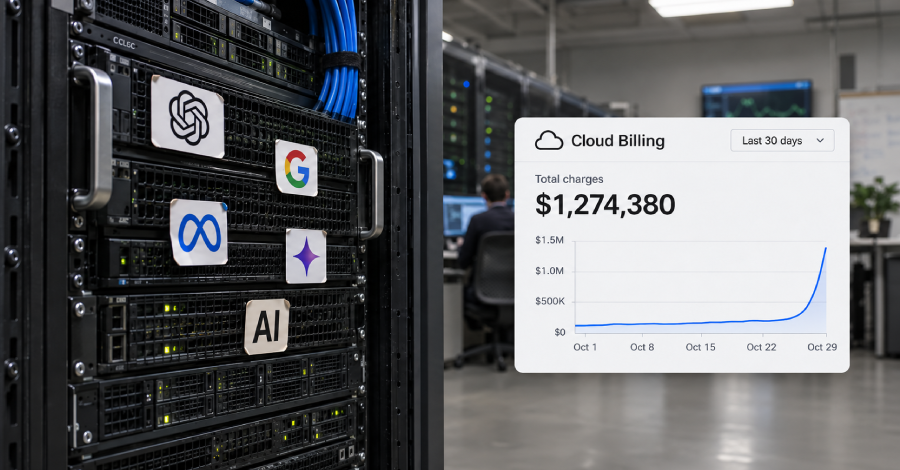
"Unlike the gradual resource consumption associated with cryptojacking, LLMJacking can generate large spikes in fraudulent cloud charges in a matter of hours," Google Threat Intelligence Group and Mandiant said in a report shared with The Hacker News.
"Across individual incidents, we observed fraudulent charges associated with resource consumption exceeding $100,000 USD in a single day, with cumulative charges at some organizations reaching $1 million USD before access was revoked."
On one end of the spectrum are low-level resource theft that involves the manipulation of customer support chatbots to conduct unauthorized tasks like code generation. LLMjacking is on the other end, as they target the backend model resources directly by identifying publicly exposed LLM endpoints or obtaining valid LLM API keys.
The most common initial access vector has been exposed or stolen cloud identity tokens, including IAM credentials, Service Account keys, GitHub Personal Access Tokens (PATs), and active session tokens, which allow an attacker to establish an initial foothold into target organizations' infrastructure.
Source link