A maximum-severity security flaw impacting Siemens SIMATIC IoT2050 Advanced devices has come under active exploitation, VulnCheck has revealed.
The vulnerability, tracked as CVE-2026-58115 (CVSS score: 10.0), is a case of missing authentication for a critical function that could be exploited by an unauthenticated remote attacker to run arbitrary code.
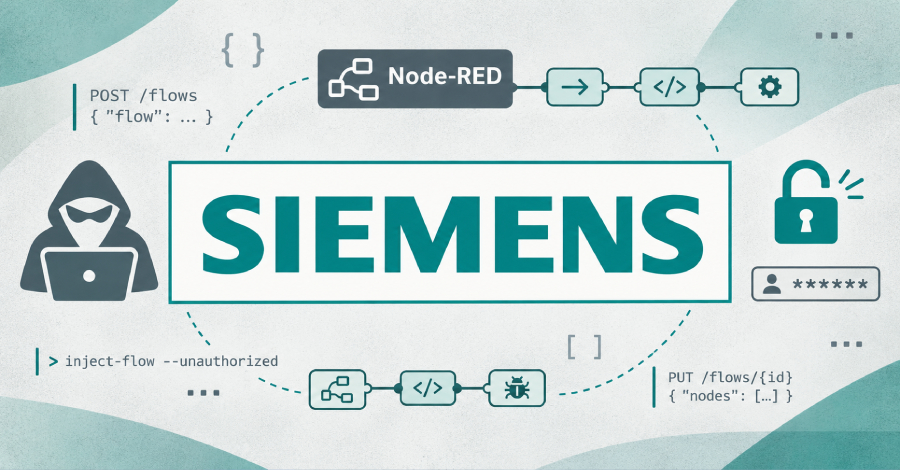
"SIMATIC IoT2050 Advanced devices running Industrial OS with Node-RED installed contain a missing authentication vulnerability in the Node-RED HTTP interface that could allow an unauthenticated remote attacker to create malicious flows and execute arbitrary code on the underlying server with maximum privileges," Siemens said in an advisory released back in August 2026.
The issue has been remediated in versions 4.3.4.1 or later. As mitigations, Siemens recommends that users uninstall Node-RED or harden the installation by following the steps below -
As of October 30, 2026, VulnCheck said it observed attackers attempting to weaponize CVE-2026-58115 against its honeypot network in an attempt to download and run a Linux bot.
"The attacker's request was a complete exploit," VulnCheck researcher Patrick Garrity said. "It deployed a Node-RED flow, triggered it automatically, and pulled a binary from an attacker-controlled server, all behind three layers of encoding."
Specifically, the malicious flow is designed to run a shell script wrapper, which uses wget to retrieve the botnet binary for AMD64 architecture from 85.215.73[.]250. Curl is used as a fallback if the wget attempt fails. In the final stage, the binary is saved as "/dev/shm/.b" and executed.
sh") from the same server.
Source link