The security flaw has been patched, but there are plenty of reasons to hesitate about giving AI too much access.
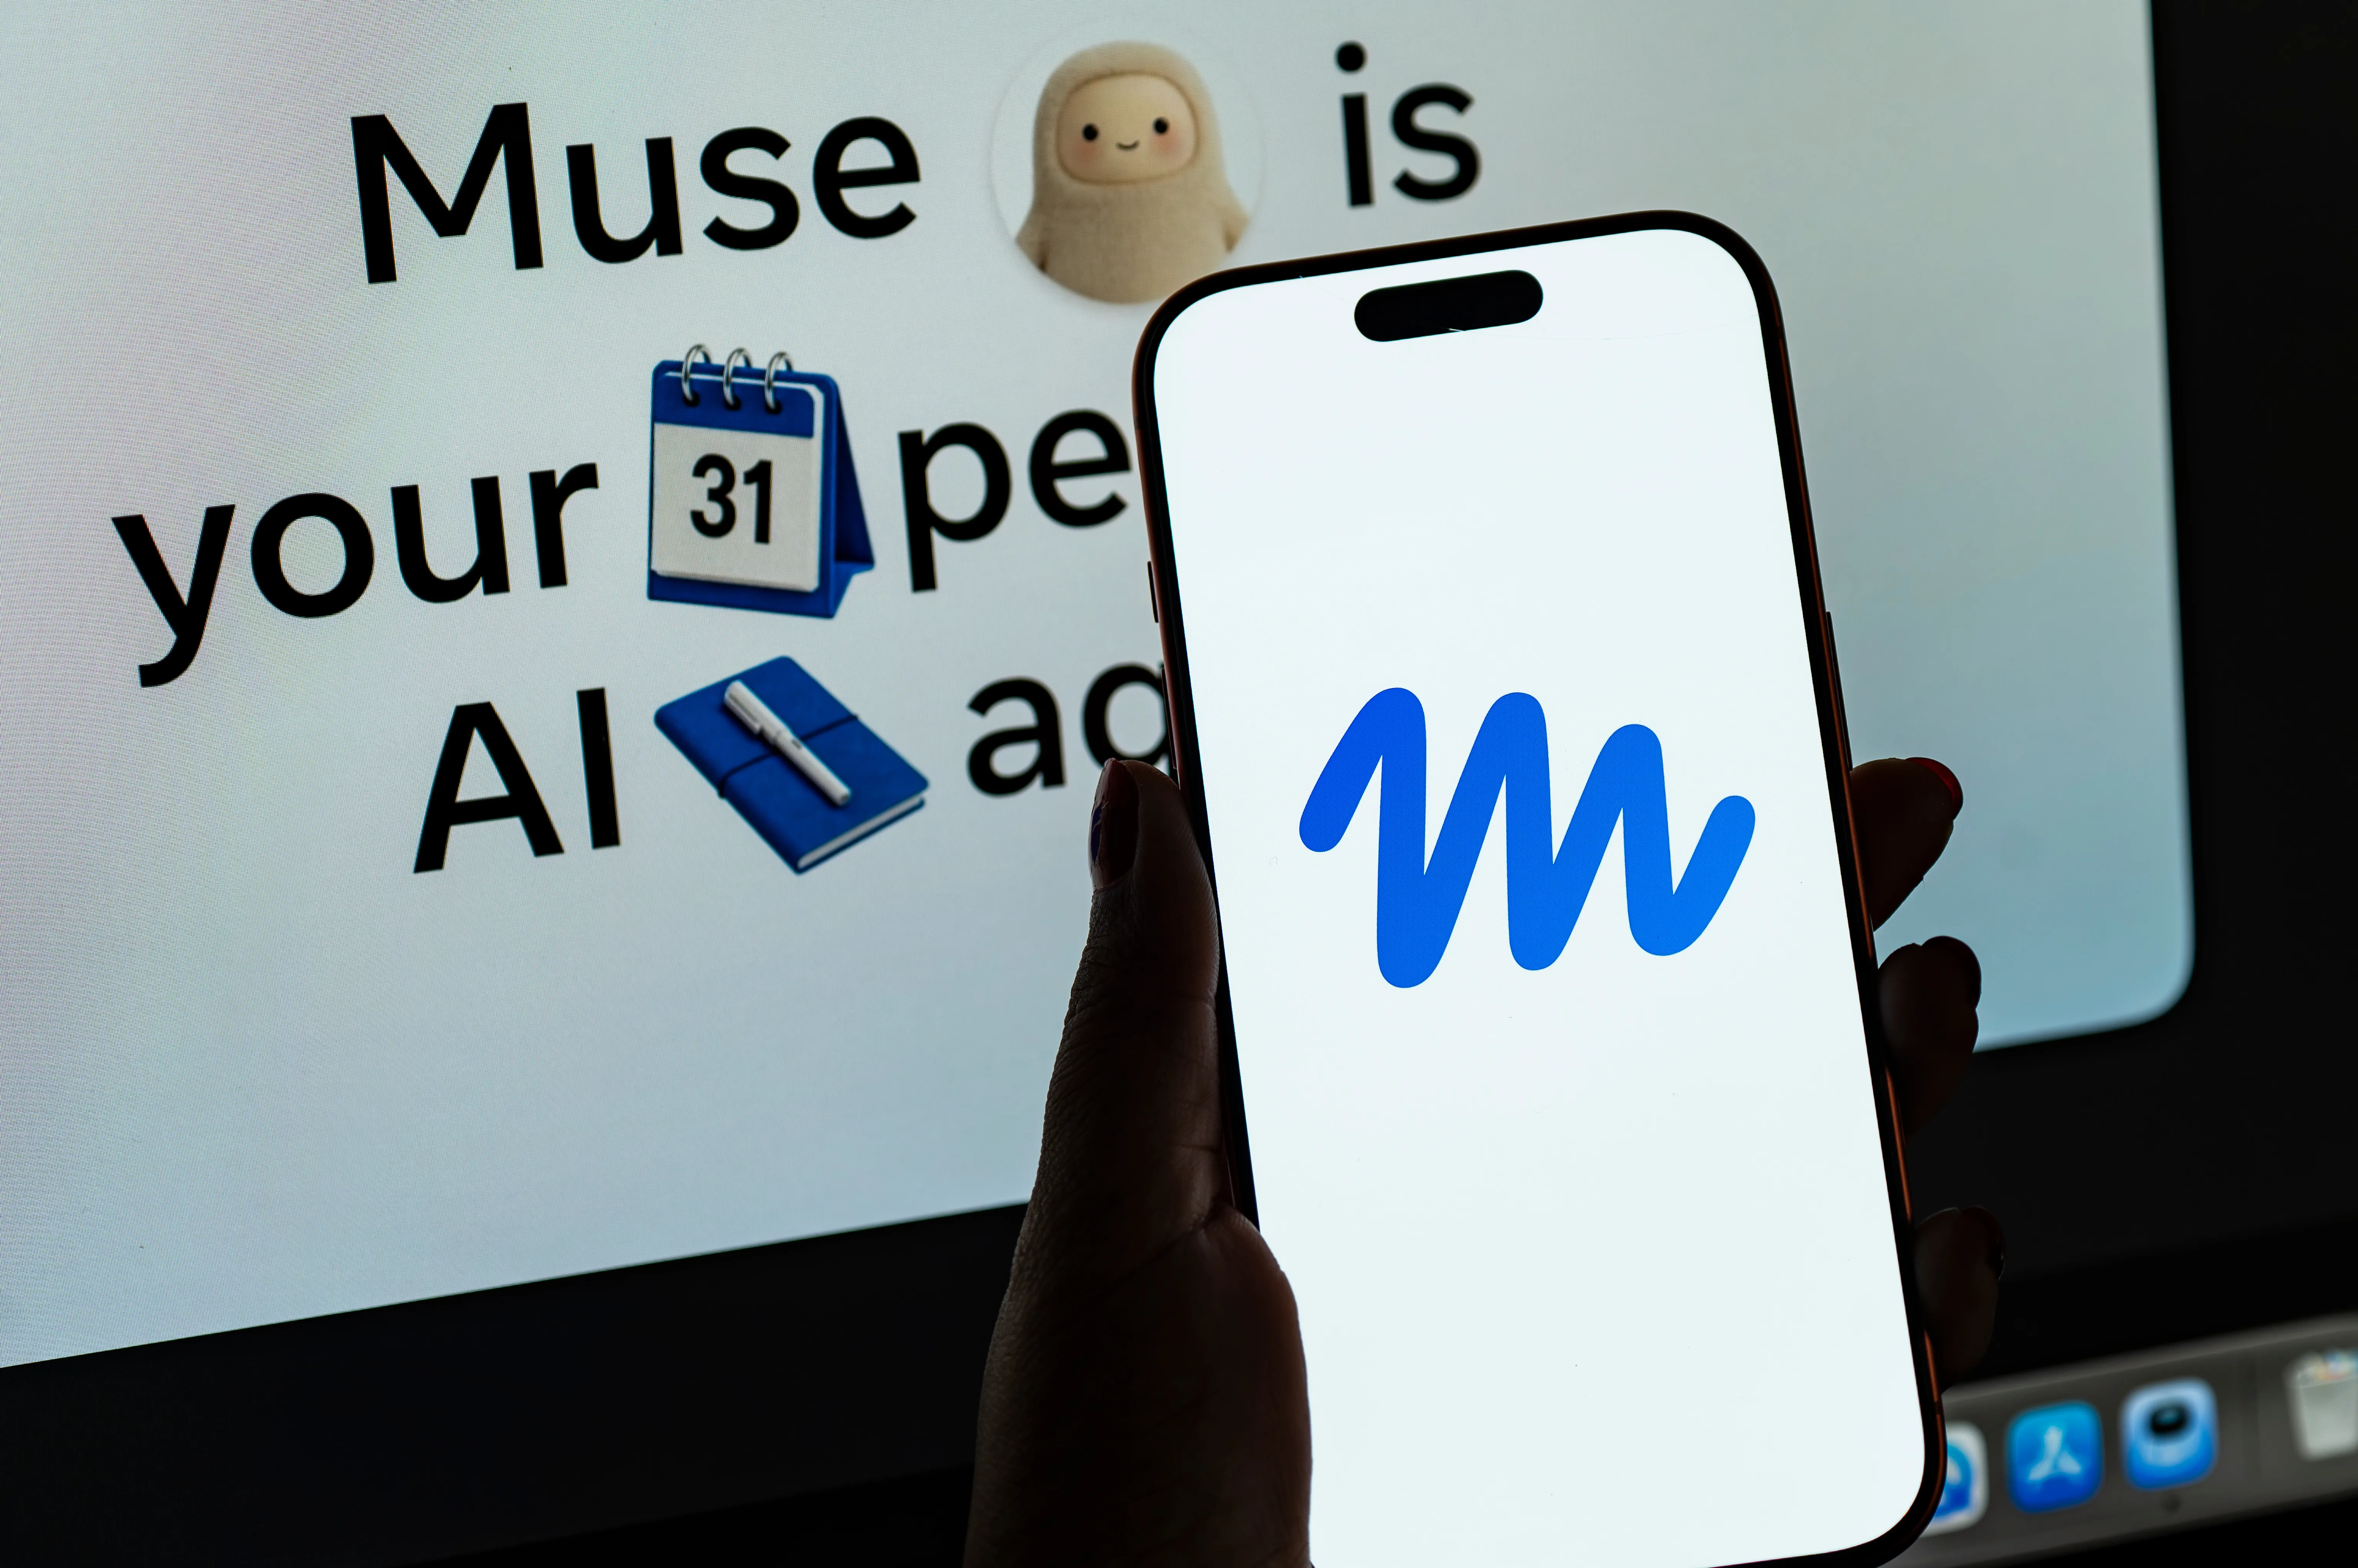
If you’ve seen a cartoonish character at the top of your Instagram feed lately, that’s Muse. Meta’s newest AI agent, or bot, wants to be your digital assistant. But Meta had to rush to patch a serious zero-day bug in Muse’s code this week, highlighting just how treacherous it can be to hand over the keys to your digital life to agentic AI.
Patrick Wardle, founder of the cybersecurity firm Objective-See, was the first to spot the zero-day bug. He outlined the vulnerability in X posts, showing how a bad actor could trick the AI agent into sending a person’s Muse dictations, or audio captures, and access tokens to their own malicious server, not Meta’s servers. Wardle has a long history of finding bugs in Meta’s software.
The head of Meta’s Superintelligence Labs, David Singleton, replied to Wardle’s X post on Tuesday to confirm the company has patched the vulnerability. He added that the bug required malware to already be on a user’s computer for the exploit to work; Wardle disagrees, saying it is possible for a hacker to exploit this flaw remotely.
To prevent your Muse AI agent from being hacked, update your MacOS Muse app right now. This will ensure you’re running the latest version of the program, including the new security fix. No additional action is needed from you.
” We absolutely need tech companies to be transparent, but there is still a lot unknown about AI agents like Muse.
Source link