For a long time, cybersecurity has often been treated as the last thing to build, applied to a platform that was already built and is serving customers. Now the approach is breaking down. The vulnerabilities are discovered and exploited faster than bolt-on controls can respond, leaving for organizations no time to catch up. The EU Cyber Resilience Act is making security-by-design a condition of market access: from 11 June 2026, EU countries must have regulatory bodies in place to certify compliance, and from 11 September 2026, manufacturers of digital products must report actively exploited vulnerabilities and severe incidents. The scope of the changes isn’t limited to Europe. A CERT-In advisory in April warned that advances in frontier AI are expanding attackers' capabilities. Indian enterprises respond by focusing their cybersecurity budgets towards identity protection, AI governance and continuous monitoring. The changes occurring in different landscapes point toward the same direction: security should be built in from the start, becoming an integral component.
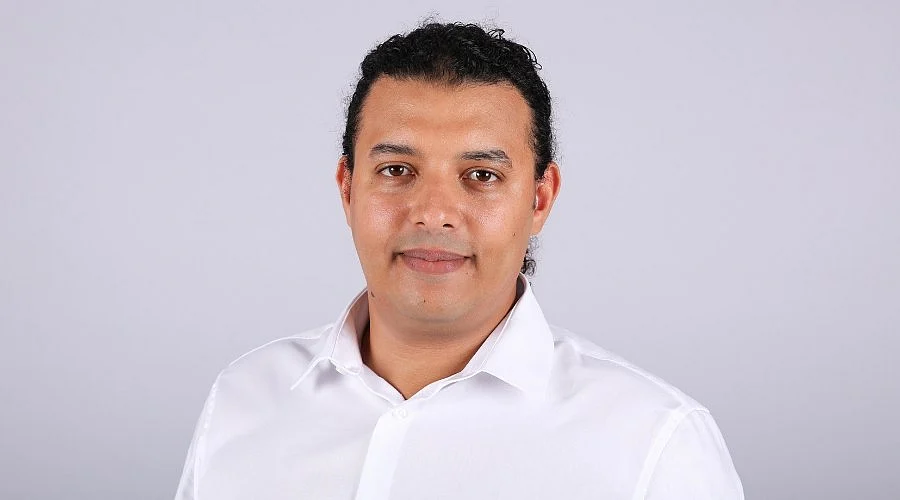
Zakaria Abidi has spent more than 18 years working inside this shift, building and governing the architecture behind systems that could not simply be redesigned from a blank page. At DigiPaye, he built and structured the company’s engineering organisation from the ground up, defining the technical standards, development processes and delivery methodology behind its SaaS payroll platforms. At INERIS, the French National Institute for Industrial Environment and Risks, he leads enterprise architecture behind the institute’s national research and public-service digital transformation initiatives.
Such regulatory deadlines require from architecture teams something more complicated than filling out a security checklist.
Source link