Can a bank know exactly who its customer is and still miss a scam? Increasingly, the answer is yes.
Social engineering and authorised scams often involve real customers using their own accounts to move money.
A customer may pass authentication and personally approve the transfer even though someone else has manipulated the decision.
According to Singapore Police’s Annual Scam and Cybercrime Brief 2025, 81.8% of scam cases in 2025 involved customer-authorised transfers, with victims typically manipulated into making the payment themselves rather than losing direct control of their accounts.
Malaysia faces its own costly version of the problem, with Bank Negara Malaysia putting the reported impact of financial fraud at RM2.8 billion in 2025 in its Annual Report 2025.
Such cases are forcing banks to look beyond whether the person behind a payment is genuine.
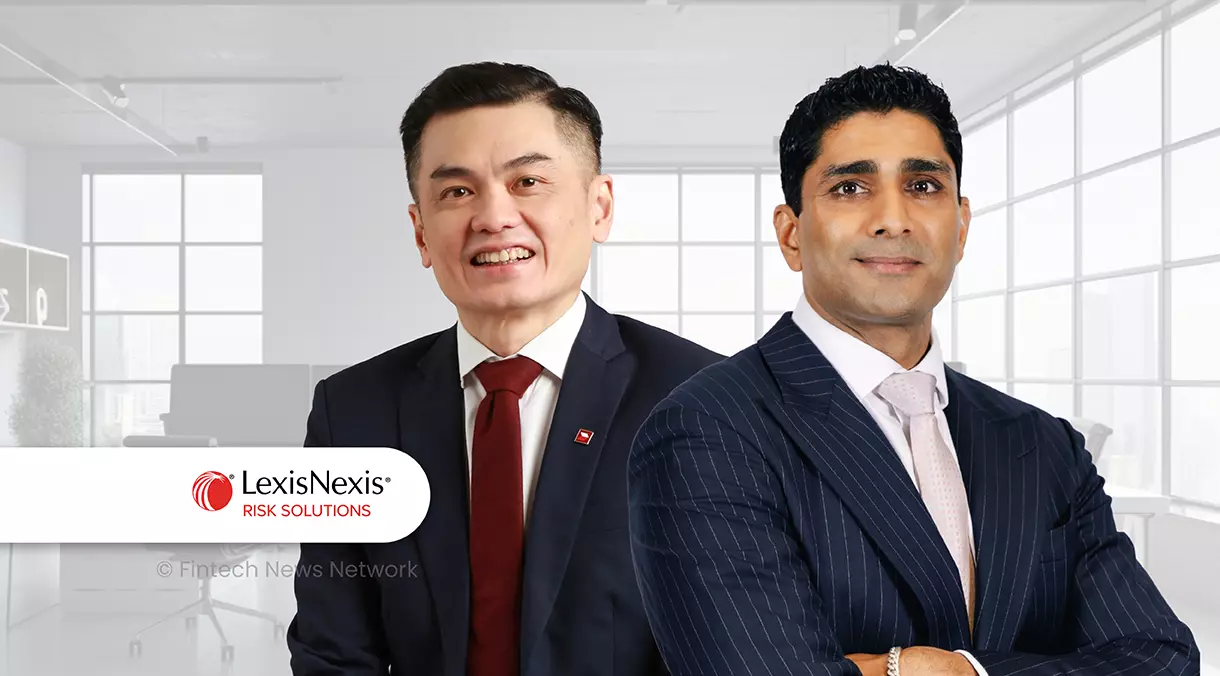
Fintech News spoke with Vishal Verma, Senior Director for APAC at LexisNexis Risk Solutions, and Keen Yew Kwan, Chief Legal & Compliance Officer at CIMB Group, about how banks assess risk when legitimate customer activity can still be linked to a scam.
“When the customer is genuine but may be acting under the influence of a scammer, identity alone is no longer sufficient.”
Authorised scams expose a wider problem once the money leaves the victim’s account.
A genuine customer may make the transfer, but the funds must then pass through several mule accounts as part of a wider laundering network.
Banks therefore need to understand what happens beyond the original payment, rather than assessing the transaction on its own.
Source link