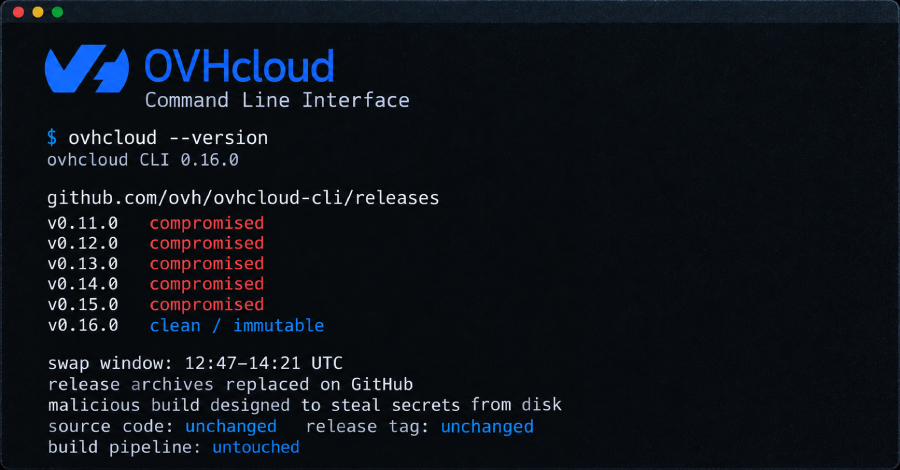
An attacker used a contributor's GitHub account to replace the download archives on five existing releases of OVHcloud's command-line tool on Monday, October 19. The account had been hijacked, and the new files were a build designed to steal secrets stored on the disk of any machine that runs it, the cloud provider says.
They were live on GitHub for up to 94 minutes, from 12:47 to 14:21 UTC, and reached only people who installed or updated the OVHcloud CLI during that window, via a path that checks for no hash, on macOS, Linux x86_64 or arm64, or Windows x86_64.
OVHcloud deleted the swapped archives and published a clean v0.16.0 that evening as an immutable release, whose files GitHub will not let anyone change. The source code, the release tag, and the company's build pipeline were not touched: the bad build was a plain go build of a later commit, uploaded straight onto releases published between April and September.
On v0.15.0, the attacker replaced six files: the macOS x86_64 and arm64 archives, the Linux x86_64 and arm64 archives, the Windows x86_64 archive, and the checksums.txt file, so the published hashes matched the new binaries. The same six files are now gone from v0.11.0 to v0.14.0 as well. The Linux i386, Windows i386, Windows arm64, and WebAssembly builds were left alone on every release.
0 as clean. Those five releases were published between April 14 and September 16, so a copy installed before 12:47 UTC on Monday and not updated since is the original.
Source link