Cybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that's being used to distribute malware such as Legion Loader.
According to Forescout Research - Vedere Labs, ROMULUS is akin to a malware delivery service that employs ClickFix-style lures on bogus landing pages to trick unsuspecting users into running malicious commands and infecting their own machines.
"ROMULUS may be a privately operated panel, a commercial cybercriminal delivery service, an affiliate framework, or software that has been copied between operators," security researcher Sai Molige said in an analysis.
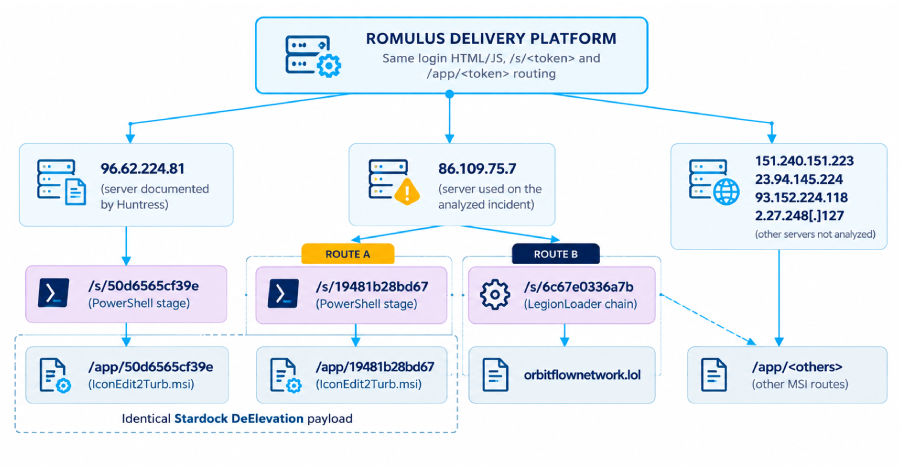
The cybersecurity company said it identified six IP addresses running ROMULUS -
Notably, the IP address "96.62.224[.]81" was identified as hosting a ClickFix script and an MSI installer file in connection with another campaign that has been found to leverage malicious ChatGPT Custom GPTs to direct victims to a fake URL responsible for serving the ClickFix lure.
Forescout's own analysis has since uncovered the same malware being delivered via another server, 86.109.75[.]7, that also hosted a panel codenamed ROMULUS. In addition, a separate chain triggered via ClickFix has been used to run a PowerShell script, which then delivers Legion Loader, a malware loader also called Satacom downloader, CurlyGate, and RobotDropper.
As of writing, it's not known who is behind the ROMULUS platform. 0), DcRAT , and potentially Venom RAT via DLL sideloading techniques.
Source link