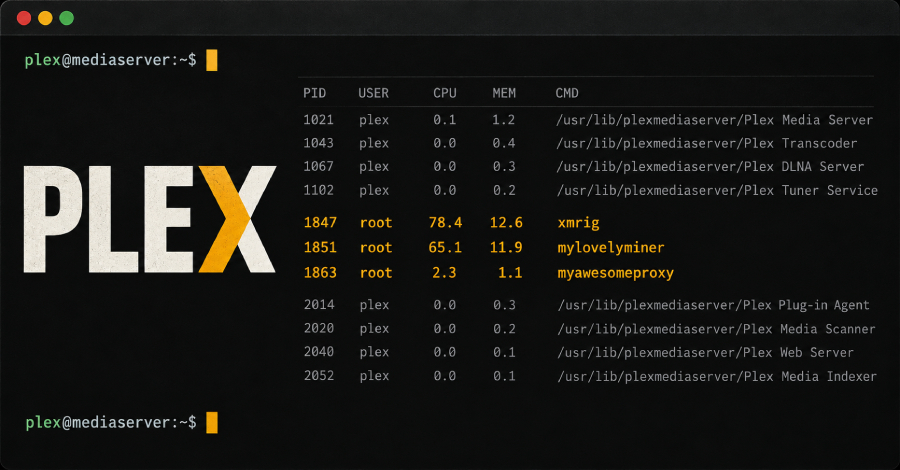
Threat actors have begun to exploit a chain of vulnerabilities in Plex Media Server to deploy cryptocurrency miners and reverse proxy software, a day after a proof-of-concept (PoC) went public.
According to a researcher who goes by the online alias boredhackerblog, the exploitation activity involves chaining four different vulnerabilities, collectively called Plex2Shell.
Put differently, the vulnerabilities can be combined together in this order to achieve unauthenticated remote code execution on susceptible Plex Media Server instances.
The vulnerabilities, along with CVE-2026-96651 (CVSS score: 7.1), were disclosed to Plex on July 27, 2026, by security researcher Zach Main, and were patched in Plex Media Server 1.43.3.10861 released on August 3, 2026.
In-the-wild exploitation attempts targeting the flaws have since been recorded a day after technical details of the Plex2Shell chain went public on October 16, 2026. The attacks led to the deployment of a miner payload from a remote server ("217.60.194[.]116").
The attack efforts have been observed from the following IP addresses -
Furthermore, the vulnerabilities have been exploited to deliver an artifact named "myawesomeproxy," which, according to VirusTotal, is a stealthy Linux backdoor and reverse proxy. Running the program displays the below message, per boredhackerblog -
Running this software on any of your devices makes you agree to the potential external use of your internet traffic.
]st ," was flagged by Bitsight in August 2026 in connection with the AISURU DDoS and proxyware botnet .
Source link