Two critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week.
Langflow is an open-source tool for building AI agents and workflows, and its vulnerability reports go to IBM. Every release from 1.0.0 through 1.12.8 has the flaws, and the only fix is version 1.13.0.
Neither flaw is in CISA's Known Exploited Vulnerabilities catalog, as of the catalog's October 30 update. Six other Langflow flaws are listed there, most recently CVE-2026-9198, which was added in August.
The four Langflow flaws in IBM's bulletin, first published on October 28 and updated the next day, are:
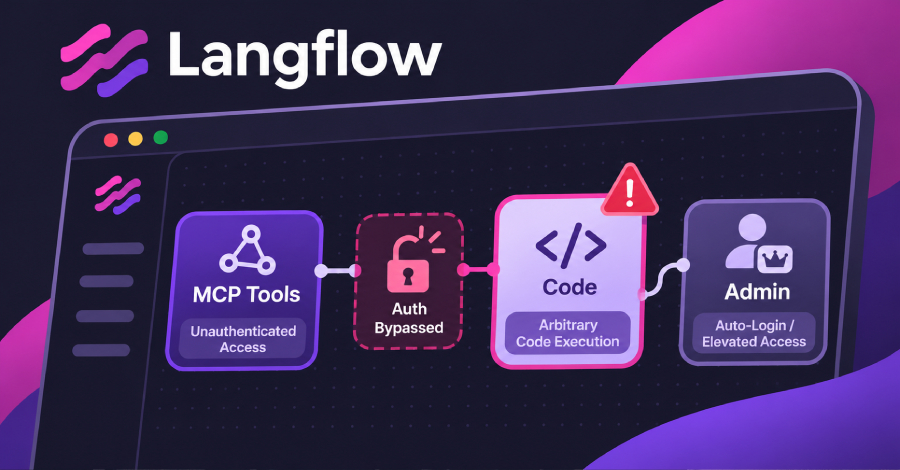
One of the flaws is "unauthenticated remote code execution exploitable through model context protocol tool enumeration," according to IBM. Through the Model Context Protocol (MCP), Langflow can offer its flows as tools to AI apps that support MCP.
A module in the public Metasploit Framework already cites CVE-2026-93680, the authentication bypass. It connects to a Langflow server's MCP endpoint without credentials, starts a session, and lists the tools the server offers. It does not run code or commands on the server.
Its author lists Langflow 1.5.0 through 1.11.4 as affected, a narrower range than IBM's.
When automatic login is enabled, Langflow logs users in as superusers without prompting them to sign in. The setting LANGFLOW_AUTO_LOGIN is enabled by default in Langflow 1.12.8. Its code description warns that it "bypasses authentication and should only be used in development environments."
Source link