Cybersecurity researchers have disclosed details of a cyber espionage campaign specifically targeting Linux infrastructure associated with government entities and state-affiliated infrastructure.
The activity, observed by Palo Alto Networks Unit 42 between October 2025 and April 2026, has been tracked under the moniker CL-UNK-1211, where "CL" refers to cluster and "UNK" stands for unknown motivation.
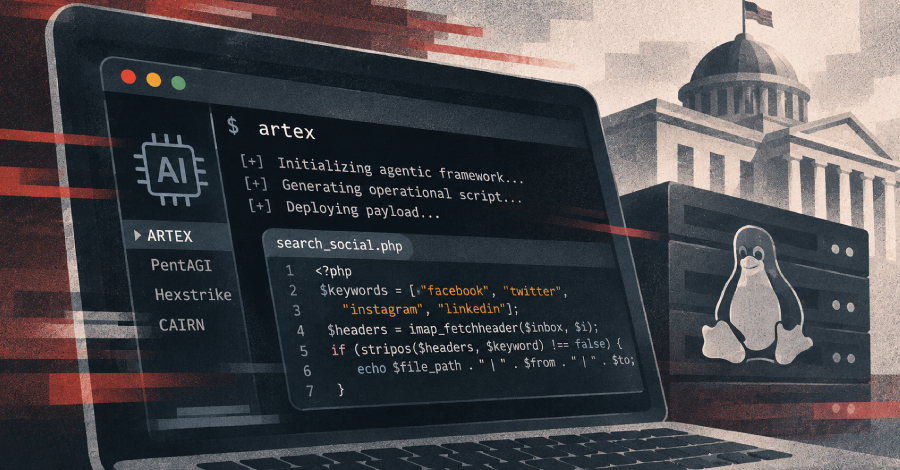
A notable aspect of the campaign concerns the use of large language models (LLMs) and/or automated artificial intelligence (AI) agents to generate payloads and execute malicious code.
"The attackers behind this cluster of activity focused on Linux environments to conduct extensive reconnaissance and maintain persistent network access to support intelligence-gathering," researchers Roey Porat and Tom Fakterman said. "The attackers attempted to dump sensitive databases and exfiltrate government mailboxes to access social media accounts."
The campaign employs a "versatile operational playbook," leveraging a combination of open-source tools, custom cross-platform backdoors, and web shells to maintain access. Another hallmark involves attempts to disable endpoint protections, wipe system logs, and plant deceptive red-team markers so as to disguise the activity as a legitimate security assessment.
The threat actor has also been observed using malicious PHP and shell scripts, likely generated using AI, to maintain persistence, perform reconnaissance, and exfiltrate data.
"Rather than standard developer documentation, multiple scripts contained conversational, step-by-step reasoning notes. These notes explained the code's logic to the operator who provided the initial instructions," the cybersecurity company said.
Source link