A non-default trust setting gave incoming Tor peers exemptions from attack limits and privacy protections. Fixes have been available since October 2025.
Bitcoin Core disclosed a configuration flaw on Nov. 10 that caused thousands of reachable Bitcoin mainnet nodes to treat incoming Tor connections as trusted peers, giving them exemptions from denial-of-service limits and privacy protections.
The project rated CVE-2025-62860 medium severity. It affected vulnerable releases when a non-default -whitelist setting covered the IP address of the node's Tor daemon, the software handling its Tor connections. Nodes that never enabled that setting were never affected.
The fixes shipped in October 2025. The new disclosure explains how a configuration intended for trusted connections spread through bundled software and granted those privileges to remote Tor peers.
For an incoming Tor connection, Bitcoin Core sees the Tor daemon's IP address rather than the remote peer's actual network address. That daemon usually runs on the same machine or local network.
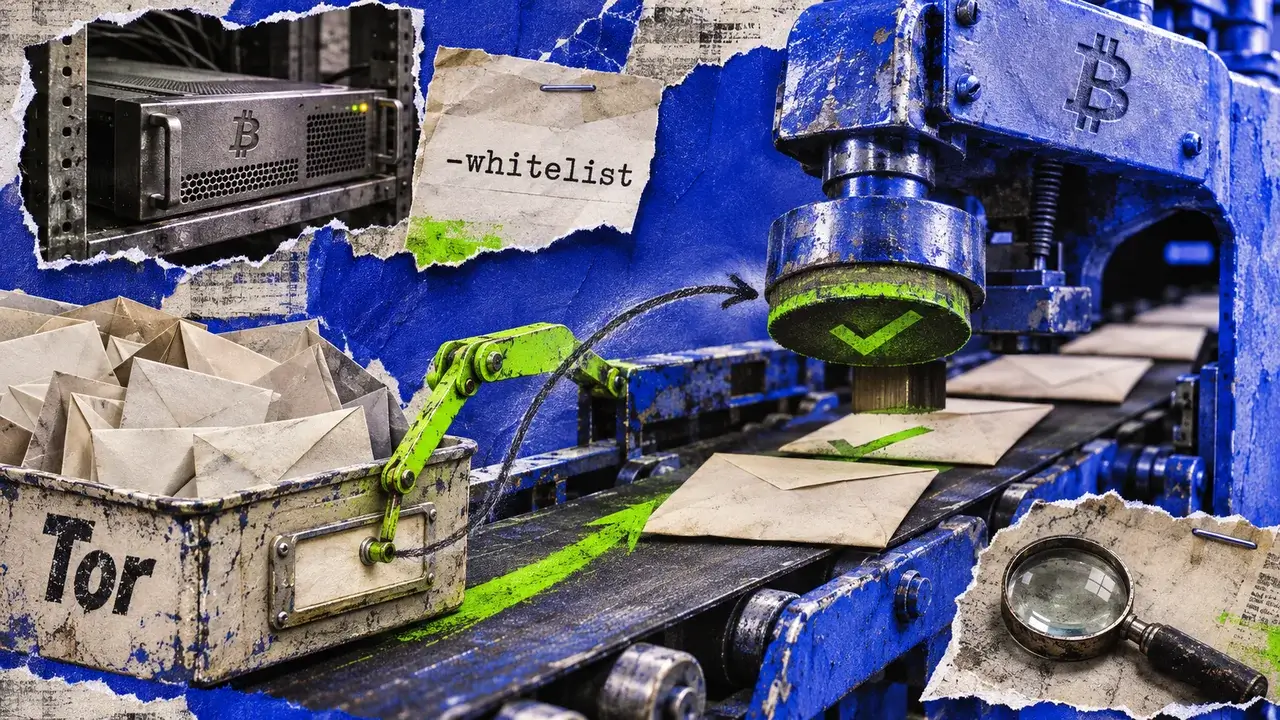
On affected configurations, Core checked that address against an IP range marked as trusted. If the range included the daemon, incoming Tor connections inherited the whitelist permissions. The local address identified the intermediary carrying the connection, but could not establish which remote peer deserved trust.
On vulnerable configurations, an IP whitelist trusted the local Tor daemon's address and passed exemptions to incoming remote peers.
A vulnerable release used the daemon's matching IP range to grant trusted-peer exemptions.
Before-fix state requires a vulnerable release and a non-default whitelist matching the Tor daemon. The change concerns address-based -whitelist permissions, not every possible peer permission.
Source link