The latest incident follows attacks involving SecuX, Coldcard and Ledger, exposing vulnerabilities beyond hardware wallets' offline protections.
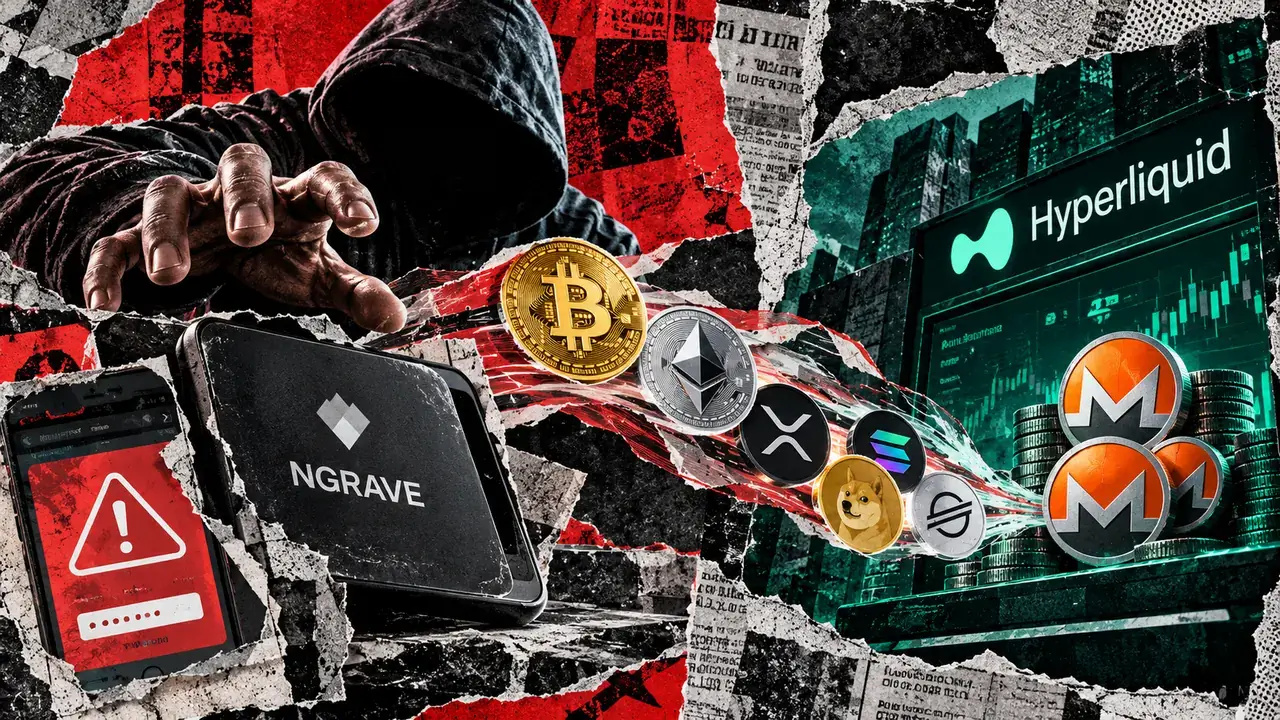
Hackers routed $2.16 million in suspected NGRAVE phishing proceeds to Hyperliquid after hijacking the wallet maker's app notifications.
Blockchain analytics firm Bitquery traced approximately $2.65 million in suspected losses across 84 cryptocurrency wallets following the Oct. 17 attack, which exploited security notifications sent through NGRAVE's LIQUID companion app.
The thefts occurred over roughly six hours across Bitcoin, XRP, Ethereum, Solana, Dogecoin and Stellar. Bitcoin accounted for the largest share, with attackers draining about $1.76 million from 21 wallets before moving the proceeds across multiple blockchains.
Bitquery traced much of the stolen Bitcoin through 12 Chainflip swaps, while Ethereum and Solana proceeds passed through bridges before converging on 39 Hyperliquid accounts.
The accounts then purchased about 3,593 XMR1 tokens, a cryptocurrency that tracks the price of privacy-focused Monero, for $2.16 million.
As of Bitquery's latest recorded check on Oct. 19, the tokens had neither been sold nor withdrawn. Their combined value was about $2.12 million, leaving a substantial portion of the suspected proceeds concentrated in identifiable accounts.
The investigation identified the suspected victims through transaction patterns and reported losses, although other phishing attacks may have affected some of the 84 wallets.
In an Oct. 19 incident report, NGRAVE confirmed that attackers compromised access to a third-party service responsible for delivering LIQUID push notifications.
Start with the stories that matter. Get the context behind the headlines and a clear view of what to watch next.
Source link