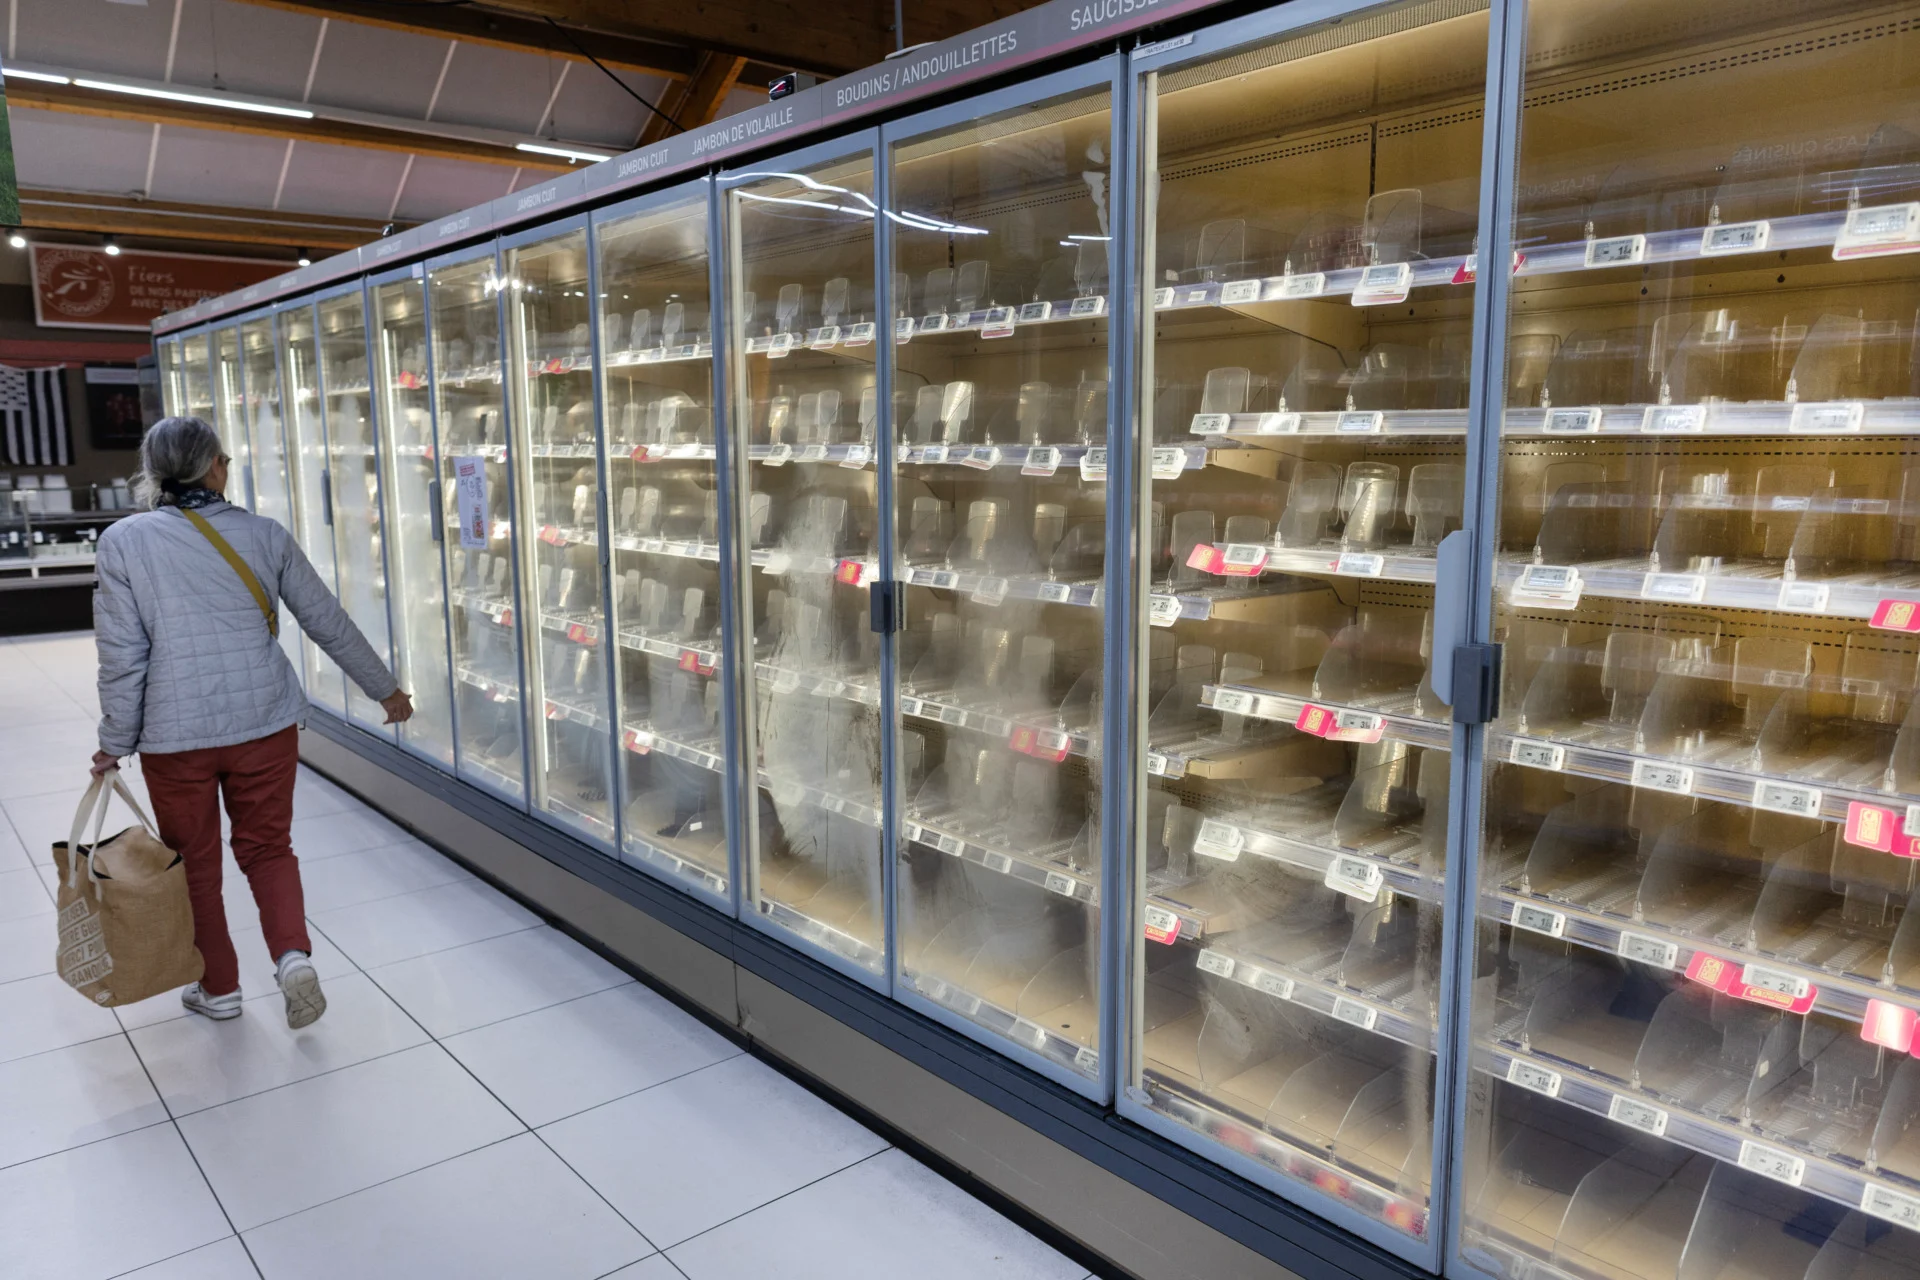
Unknown hackers breached hundreds of supermarkets across France this weekend and remotely raised thermostats on fridges and freezers up to 122 degrees Fahrenheit (50 degrees Celsius), spoiling huge amounts of food, French authorities told Reuters. Paris prosecutors say the attack is “large-scale.”
The full extent of the damage is unclear, but both food spoilage and fires have reportedly been the result. Intermarche CEO Thierry Cotillard said on BFM TV that they’re likely in the tens of millions of euros, according to Reuters. A source with Prime Minister Sebastien Lecornu’s office told Reuters that France’s National Cybersecurity Agency (ANSSI) is investigating and already found signs the attack originated with a vulnerability at Danish engineering firm Danfoss.
In a statement to Reuters, Danfoss wrote that the company is “aware of incidents in France affecting a limited number of refrigeration management systems.” By Reuter’s count, confirmed targets include Intermarche owner Les Mousquetaires (150 stores), Carrefour (80 stores), Monoprix (around 5% of its 490 stores in France, or ~25), and Cooperative U (unclear). Sekoia Threat Detection and Research senior cyber intelligence threat analyst Felix Aime told the news agency other organizations in Spain, Portugal, Poland, Germany, and Belgium appeared to be hit.
Targeting the retail sector is far from uncommon—an attack on UK retailer Marks & Spencer last year that shuttered stores and caused £324 million ($428 million at current exchange rates) in lost sales was just the start of a spree that eventually snared brands like Harrod’s.
It’s often the case that operational technology (OT) systems that end up connected to the internet weren’t designed with security in mind , and disabling equipment with the intent of causing costly downtime is a common pressure point for ransomware gangs and other threat actors.
Source link