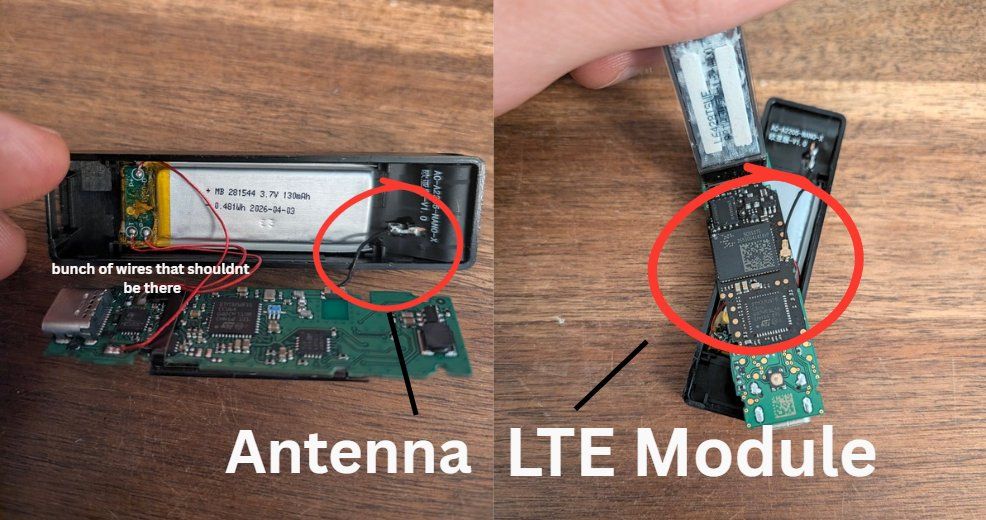
Ledger is reviewing its sales policies and how its devices reach customers after the “Cryptobilis incident,” in which physical tampering along its supply chain led to $93 million in cryptocurrency theft from user wallets, according to a Bloomberg report on October 13. The crypto hardware manufacturer’s CTO, Charles Guillemet, confirmed in a social media post that it is also reviewing anti-tampering protection on its devices following the incident. He told users with tampered signers (hardware wallets) to contact Ledger support for shipping instructions to send the devices in for further examination. Guillemet also advised users who wanted to physically open their signers to check for tampering to review the company's guidelines on how to do so safely.
In a separate post, Ledger CEO Pascal Gauthier said, “Physical supply chain tampering is a risk for the whole industry. We are reviewing the controls that apply to our direct sales and to resellers, and we will share what we can,” confirming the company's plan to review its chain-of-custody and tamper detection practices. The company is inviting researchers and other vendors to collaborate in assessing these practices.
The incident that prompted the reviews was first noticed on Friday, October 9, when hundreds of otherwise secure wallets drained simultaneously across the Bitcoin, Ethereum, and Tron networks, triggering a massive alert across social media and blockchain security networks. Several victims came online to report losses and try to figure out what was happening. Early investigation revealed that almost all the affected wallets had been procured from CryptoBilis, an authorized third-party reseller covering Malaysia and Southeast Asia.
Source link