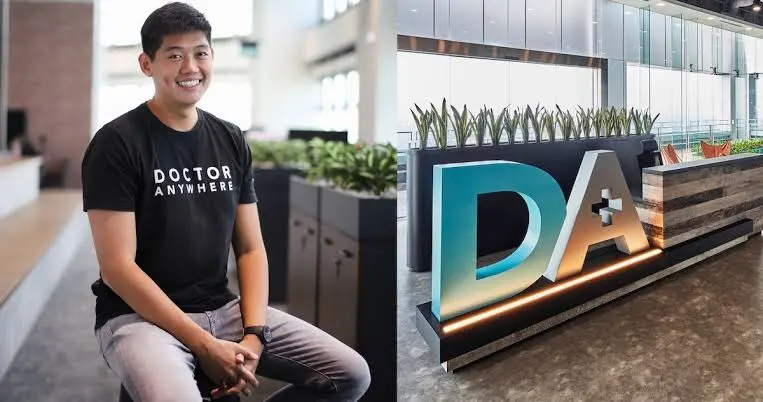
Telehealth provider Doctor Anywhere announced on Friday evening, Nov 6, that an unauthorized third party breached its systems and accessed users’ personal information.
The intrusion, which the Singapore firm discovered on Oct 29, compromised customer names, email addresses, dates of birth, emergency contacts, bank account numbers, identity card digits and passport details.
Doctor Anywhere stated that investigations have found no evidence showing passwords, account login credentials, payment card details or scanned identity card photos were compromised, though it has not disclosed how many users were affected.
Part of the compromised data involves corporate accounts held through Adept Health, a Doctor Anywhere subsidiary that manages employee benefits programs for corporate clients across Singapore. The platform keeps select personal records of corporate members inside its central architecture to administer employer coverage and process claims.
Digital health providers across Southeast Asia rely on corporate medical coverage contracts to generate recurring cash flow alongside direct-to-consumer video doctor consultations. A breach across employer benefits architecture creates immediate legal and compliance questions for human resource directors managing corporate health data.
The company engaged cybersecurity and digital forensics firm Ensign InfoSecurity to examine the network intrusion and apply corrective patches. Ensign confirmed that the discovered vulnerabilities were locked down and validated the fixes on Oct 30, according to the health operator.
Medical treatment records remained untouched throughout the incident, the provider said following initial network scans. Its digital platform, outpatient clinics and walk-in facilities remain fully operational while customer notifications continue.
Doctor Anywhere reported the breach to the Personal Data Protection Commission and lodged a formal report with the Singapore Police Force.
Source link