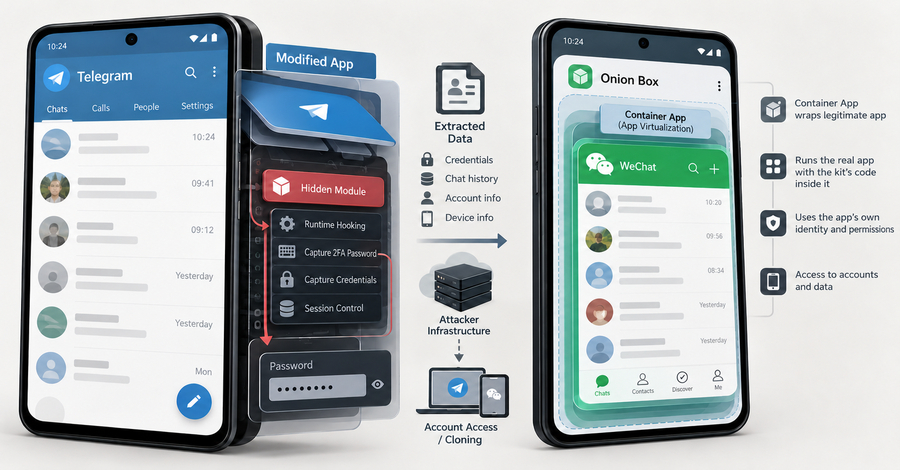
A rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies of the two apps, researcher Ovi found. It only reaches people who install one of these tampered copies, spread outside the official app stores, or who run WeChat inside the kit makers' own container app.
The kit's Telegram part matches Baohuo, a backdoor that Doctor Web reported in October 2025. Doctor Web found Baohuo in tampered copies of Telegram X, an Android app from Telegram. At the time, the company estimated that more than 58,000 devices were infected.
The Hacker News compared the two reports. Doctor Web's technical description of Baohuo lists the same code namespace, com.ucreator.tgjar, the same command-and-control (C2) server, and matching command names as Ovi's analysis.
Ovi's analysis, published October 21, 2026, does not mention Doctor Web's findings, and Doctor Web did not name the kit. It is not clear whether the kit's makers or one of their customers ran the campaign Doctor Web tracked.
The tampered apps spread through sideloading, where a person installs an app file directly instead of from an app store, and through social engineering, Ovi found. He could not confirm how every victim was infected.
A second route is the kit makers' own container app, called 洋葱盒子 ("Onion Box"), which runs other apps inside itself.
Some of the tampered Telegram X copies use the same package name as the real app on Google Play, so the name alone does not give them away.
Source link