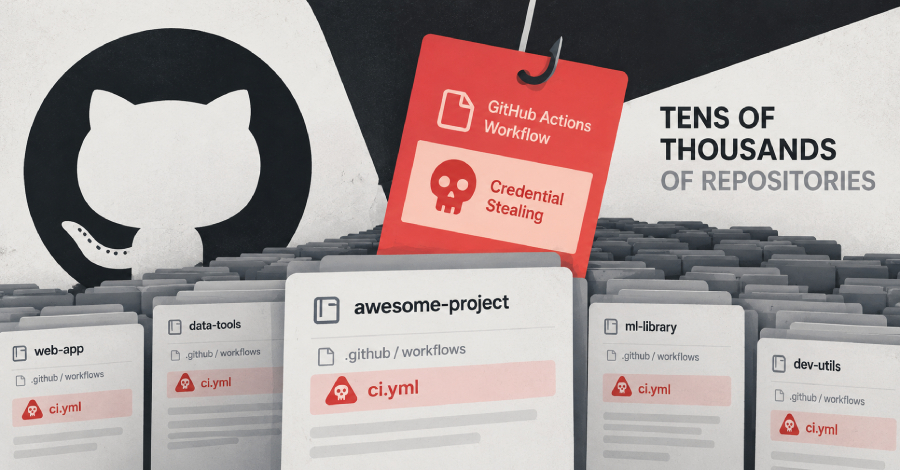
Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over 340 repositories.
"Using the account of Takashi Kitao, author of the 18,400-star game engine pyxel, the attacker pushed a malicious workflow to 27 repositories starting at 13:20 UTC," StepSecurity said. "Eight hours later, the account of Henry Wu (henrywoo), the original author of Uber's athenadriver, was used to push the same workflow to 318 repositories in a 16-minute window, 21:10–21:26 UTC."
As of October 9, 2026, Socket said it has identified more than 500 GitHub accounts that committed the malicious workflow to tens of thousands of repositories since October 7, 2026.
The activity has been attributed to GhostAction, a massive supply chain attack campaign that first came to light in September 2025. The activity impacted 817 repositories across 327 GitHub users, resulting in the exfiltration of 3,325 secrets, including PyPI, npm, and DockerHub tokens through compromised developer accounts.
Like before, both accounts have been found to push a workflow named Security Audit ("security-audit.yml") or GitHub Actions Security ("github_actions_security.yml"), which are designed to exfiltrate sensitive data to a hard-coded IP address ("193.32.204[.]199") over plain HTTP.
The captured data contains the repository's named GitHub Actions secrets, including CI/CD secrets, and cloud, AI, and SaaS credentials present in the working tree and the entire git history, such as AWS keys, Anthropic, OpenAI, and OpenRouter API keys, and GitHub and GitLab tokens.
"It triggers on workflow_dispatch and an unfiltered push (any branch, any tag), checks out with fetch-depth: 0, and runs a single 'Audit' step that does four things," StepSecurity added.
Source link