
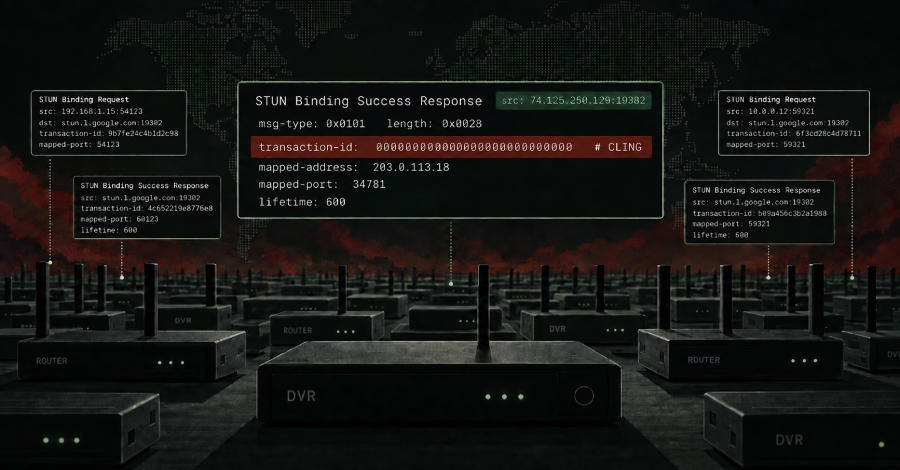
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy a botnet malware called Cling.
"Cling is notable not because it introduces a new propagation technique, but because it repurposes ordinary STUN behavior into a practical command-and-control channel," Nozomi Networks said in a report published last week. "The result is a botnet whose traffic can resemble legitimate NAT-traversal activity while still supporting propagation, proxying, tunneling and denial-of-service commands."
The operational technology (OT) security company said it observed a spike in attempts to exploit CVE-2021-35394 (CVSS score: 9.8), a critical remote code execution (RCE) flaw in Realtek Jungle SDK starting around September 5, 2026, with a subset of the activity delivering Cling.
An analysis of the malware sample has found it to embed exploit logic for various command injection and RCE vulnerabilities impacting routers and DVRs from multiple vendors -
"The single-instance check to only run one copy involves binding a socket with SO_REUSEADDR to port 33957 and exiting cleanly if it fails," Nozomi Networks said. "The sample copies itself to /root/.cling and /usr/local/bin/.cling. Both executables are appended to /etc/inittab, /etc/init.d/rcS, /etc/rc.d/rc.boot, thus achieving persistence on SysV and BusyBox init systems."
An alternative persistence mechanism involves identifying the wget binary on the infected system and then replacing it with the malware, but not before moving the original to another location. This, in turn, causes the malware to be executed when a legitimate process invokes the "wget" command.
Source link





