OpenAI on Wednesday detailed a pipeline that employed an upcoming cyber-focused artificial intelligence (AI) model to validate and patch 948 local privilege escalation vulnerabilities in Linux for $1.2 million in API costs.
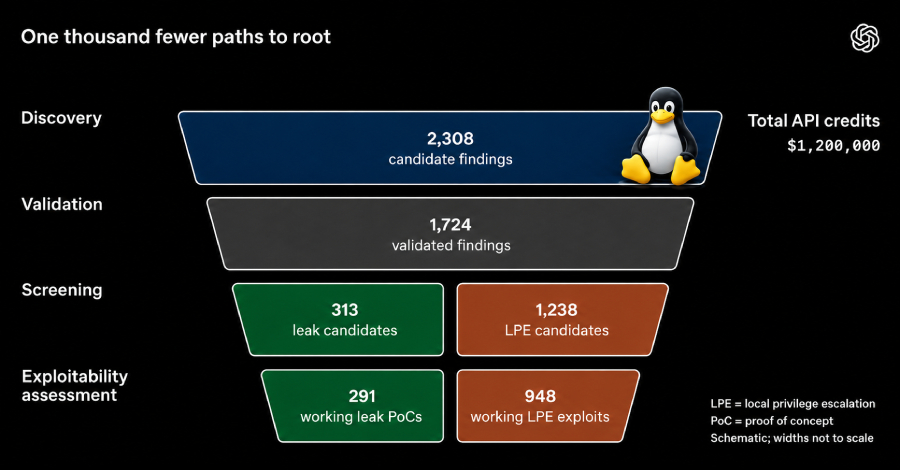
"Our prototype identified and analyzed 2,308 candidate Linux kernel findings, dynamically reproduced 1,724 vulnerabilities, and produced 948 local privilege escalation (LPE) exploits that could allow an unprivileged local user to gain root access," the AI company said.
The findings build upon 24 LPE exploits that OpenAI revealed were discovered by its GPT‑5.5‑Cyber model back in June 2026. The latest research turns this process into an agentic pipeline comprising five stages -
"In a run in mid-October 2026, our pipeline using an upcoming cyber model dynamically reproduced 1,724 vulnerabilities [within 30 hours] and generated PoCs for 291 information leak vulnerabilities and 948 working local privilege escalation (LPE) exploits for a commonly used Linux distribution," OpenAI said.
"The total run cost $1,213,430 in API credits, or $1,279 per LPE exploit. To the best of our knowledge, the agents in this pipeline discovered and used at least 10 novel Linux exploitation techniques."
The development is once again an indication of how frontier AI is redrawing the contours of cybersecurity, accelerating vulnerability discovery and exploitation, and at the same time helping defenders reliably address defects, albeit through additional instructions and iterations, before attackers can use them, and make it "cost prohibitive" for bad actors to exploit software.
In a report published last month, VulnCheck categorized AI-assisted vulnerability discovery as a "growing risk category" that turbocharges novice hackers, who now require little to no technical expertise to detect software vulnerabilities.
Source link