Cybersecurity researchers have disclosed details of what has been described as a "highly sophisticated infection chain" targeting government organizations in Asia.
The activity, detailed by Kaspersky this week, targeted a custom Windows 10 build used exclusively by government entities in Asia and involves the deployment of a previously undocumented .NET assembly-loading framework codenamed NetamLoader.
The attack has not been attributed to any known threat actor or group. Nor is it clear if the intrusion compromised more than one system and allowed the hackers to steal any sensitive information.
The Russian cybersecurity company said the artifact was detected in the first half of 2026, packaged inside a Windows cabinet archive (CAB) file placed in a directory that stores Windows operating system update packages.
It's suspected the operation involved a supply chain attack, in which bad actors compromised a trusted third-party vendor to gain access to downstream users who rely on its services or software.
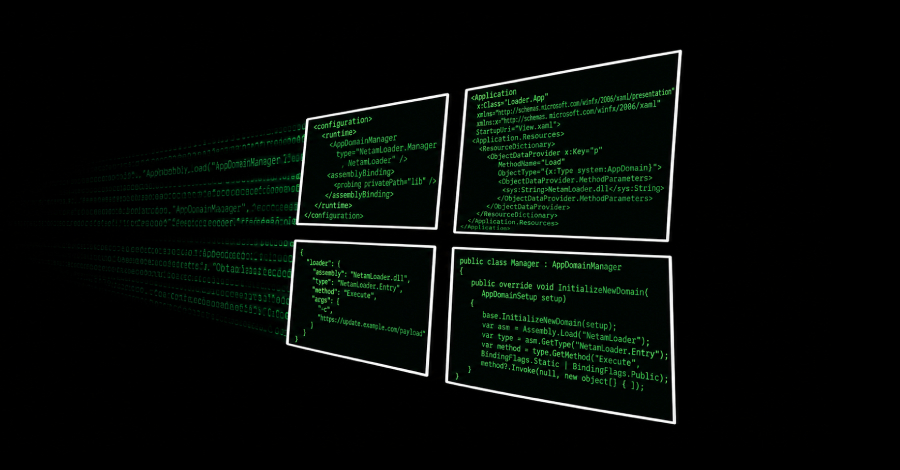
The sample in question features a ".config" file that employs AppDomainManager injection to load arbitrary .NET assemblies. AppDomainManager injection is an adversarial technique used to load arbitrary payloads by hijacking .NET Framework's AppDomainManager mechanism when a .NET application starts.
Put differently, the approach targets .NET Framework's application-domain initialization to achieve code execution. The end result is the same as DLL sideloading: to run malicious code inside a legitimate application's process so as to fly under the radar.
According to Kaspersky, the CAB archive containing the .config file was placed in the path: "C:\Windows\SoftwareDistribution\Download\e4537a1762fcafd2fd96bfc825bad34f9db9a24," with its contents extracted and dropped into "C:\Windows\SoftwareDistribution\Download\Install\."
Source link