N-able Takes N-central Cloud Offline After Researcher Discloses 33 Zero-Days with PoC Exploits
N-able said it has taken N-central Hosted Environments offline and is urging on-premises customers to shut down their servers until further notice following the public disclosure of over 30 vulnerabilities collectively tracked as Able2Shell .
"As a precautionary measure, we are temporarily taking our Hosted N-central environment offline while we take the necessary actions to secure the environment and implement appropriate remediation," N-able said .
"During this time, customers will be unable to access their Hosted N-central classic environment, and associated services may be unavailable. However, the Ecoverse services under N-able Login remain available and online, including Asset View, Patching, Vulnerability Management, scripting, policies and tagging."
The company also said it has not observed any signs of active exploitation of these vulnerabilities, adding it's currently working on a hot fix to address them.
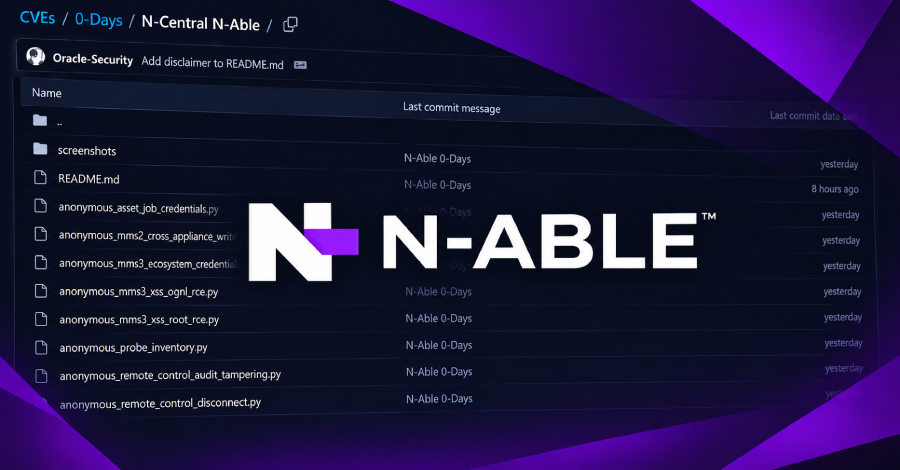
The development comes as independent security researcher Sean Bales disclosed multiple security flaws along with proof-of-concept (PoC) exploits. The researcher said the issues were tested against N-able N-central Appliance 2026.4.0.31.
The identified zero-day vulnerabilities include credential disclosure, arbitrary file writes, directory traversal, cross-site scripting (XSS), XML external entity (XXE) injection, and remote code execution (RCE) flaws -
Multiple N-central zero-days enable anonymous credential theft, administrator creation, and nable/root RCE.
Chains include XXE/NCI trust abuse, support-token theft, unsigned NSP execution, XSS-to-OGNL, and authenticated reverse shells.
Arbitrary file writes, traversal, credential disclosure, MDM impersonation, audit tampering, and privileged-helper injection.
Successful exploitation of these flaws can allow rogue administrative access to the N-central management interface and facilitate command execution as root.
Source link