The threat actor known as Blind Eagle has resurfaced with a new campaign targeting organizations in Latin America through judicial and administrative-themed phishing lures to deliver a remote access trojan (RAT) that shares its lineage with AsyncRAT and DCRat.
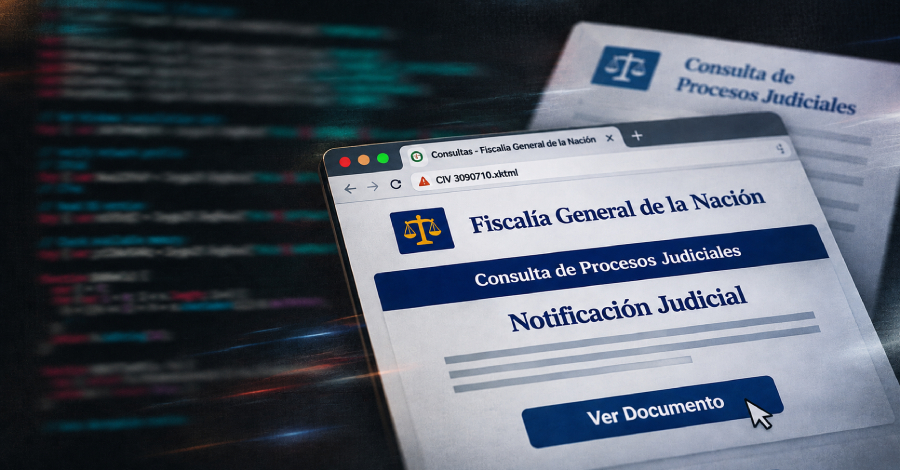
"The campaign uses Portuguese and Spanish lures that resemble court notifications, fiscalía notices, tutela proceedings, and administrative documents," Zenox said in a report shared with The Hacker News.
Assessed to be a Spanish-speaking group and active since 2018, Blind Eagle (aka APT-C-36) has a track record of using spear-phishing lures to distribute commodity RATs like AsyncRAT, BitRAT, Lime RAT, NjRAT, Quasar RAT, and Remcos RAT.
Attack chains begin with phishing emails targeting individuals who handle cases, contracts, judicial, or institutional service requests to trick them into opening a malware-laced attachment.
One email containing a Colombian judicial-themed XHTML file has been identified as a weaponized Scalable Vector Graphics (SVG) image that renders a bogus web page impersonating Colombia's Fiscalía General de la Nación, also referred to as the Office of the Attorney General.
The web page, for its part, employs a technique known as HTML smuggling to assemble the next-stage ZIP archive payload locally in the web browser using ZipCrypto, thereby circumventing email security controls.
298. The JavaScript code conducts environment reconnaissance, and collects details such as system version, network profile, installation date, memory size, computer name, environment variables, and directories localized in Portuguese and Spanish.
Source link