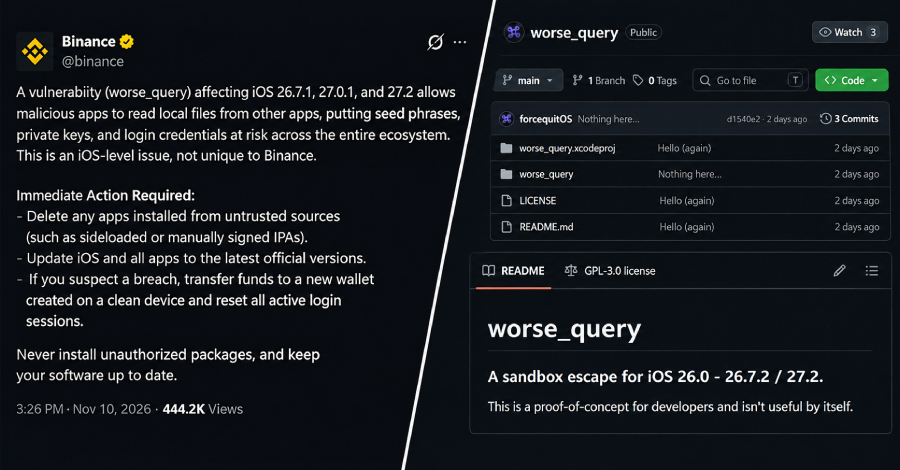
An iOS sandbox escape published on GitHub lets an app read other apps' files on iPhones running iOS 26 and 27. That puts seed phrases, private keys, and login credentials at risk of exposure to malicious apps, Binance warned today. Apple's updates for iOS 26 and 27, released yesterday, do not list a fix.
A researcher who goes by forcequit released the escape, called worse_query, on Sunday, a day before those updates came out. Neither the exchange nor the researcher reported any attacks or thefts involving it.
The exchange told users to delete apps installed from untrusted sources, such as sideloaded or manually signed apps, and to update iOS and all their apps. No fix for the escape has been confirmed.
For anyone who suspects a breach, the exchange's security warning advises moving funds to a new wallet created on a clean device and resetting all active login sessions.
The researcher's proof-of-concept code can reach every app's data container on an iPhone, and some system folders on iOS 27. To use it, an app has to set up an App Group container.
He says the code is for developers and "isn't useful by itself." Other developers have built apps on it that people can install.
One of them is WQ Files, a file manager that developer Christoph Kolbicz built on worse_query. It reaches other apps' data without a jailbreak or a kernel exploit, and it can edit, delete and clear that data.
WQ Files installs via sideloading tools such as AltStore and SideStore, which automatically create the App Group it needs when used with an Apple ID.
Source link