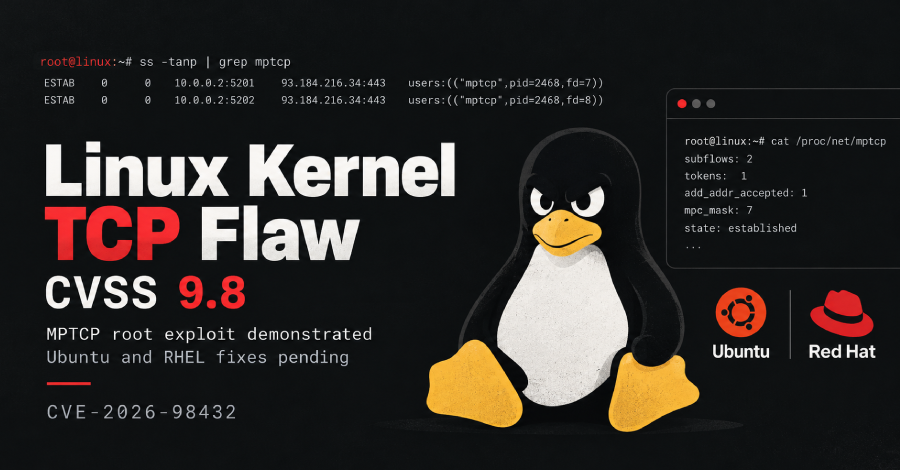
A flaw in the Linux kernel's TCP code, tracked as CVE-2026-98432, affects Ubuntu, Red Hat Enterprise Linux (RHEL), and other Linux distributions. The kernel's own CVE team rates it 9.8 out of 10 on the CVSS scale.
Anthropic said on October 27 that its AI model wrote an exploit that uses the flaw to let a remote attacker with no credentials run commands as root on Linux servers with a multipath TCP listener.
As of October 29, Ubuntu and RHEL have not released a fixed kernel. Red Hat, Amazon, Oracle, and SUSE score the flaw between 5.9 and 8.1, lower than the kernel team's 9.8.
The flaw is a race condition in the code that sets up new IPv4 TCP connections. It can make the kernel read memory it has already freed, a bug type known as a use-after-free.
The kernel fix credits Anthropic researcher Xinyang Ge with reporting the bug. Neither the CVE record nor the fix mentions multipath TCP (MPTCP). The link between that feature and this bug comes from Anthropic's post.
MPTCP lets one connection use several network paths at once. On Linux, an application must request MPTCP when it opens a socket.
Anthropic's post says the flaw "was patched upstream and backported to all maintained stable kernel branches." For distribution users, that fix arrives only in the vendor's kernel package. Debian, Oracle Linux, SUSE, and Amazon Linux have shipped fixed packages, at least for some of their kernels, but Ubuntu and RHEL have not.
Ubuntu also lists its cloud, FIPS, and real-time kernels as vulnerable or as work in progress.
Source link