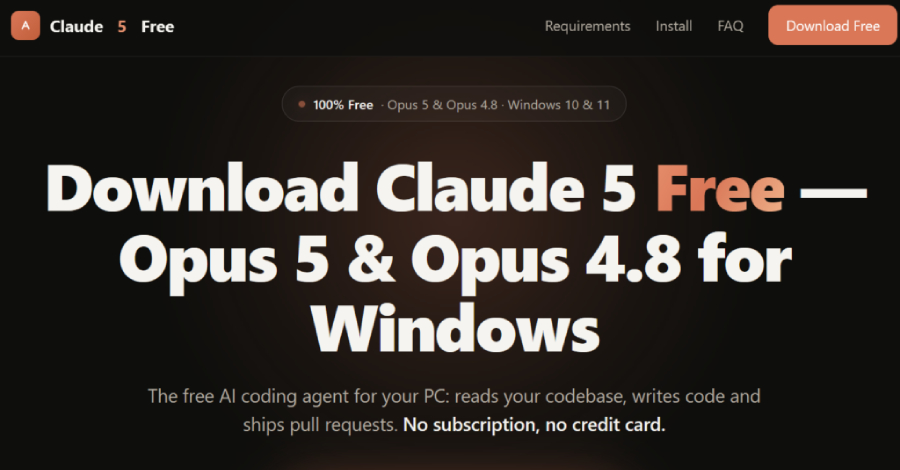
Threat actors are delivering malicious loaders and cryptocurrency miners under the guise of artificial intelligence (AI) desktop applications for Anthropic Claude and OpenAI ChatGPT as part of a campaign dubbed Yoba.
The activity involves creating fake GitHub projects that claim to be desktop applications like GPT-5.6 Sol, GPT-6 Astra, and Claude Opus, only to deliver a malware family called YobaLoader.
"The malware is placed next to legitimate, signed executables from OpenAI and Anthropic so it can be loaded indirectly, a technique commonly known as DLL sideloading, which is often used to bypass security protections," Check Point Research said in an analysis.
To add to the project's credibility, the attackers set up GitHub.io pages to describe the capabilities of the software. Although the GitHub projects' popularity is not manipulated using techniques like ghost networks, signs point to the use of SEO poisoning tactics to ensure that links to them are surfaced on top of search results on Google.
"Each repository uses a different email address (edwardcarlsonmkym[@]outlook[.]com, daxschneiderdjuu[@]outlook[.]com, and rioprestonlfyx[@]outlook[.]com), and the uploader appears to operate in UTC+4, UTC-4, and UTC+3 respectively," Check Point said. "This inconsistency likely reflects a deliberate attempt to obscure the threat actor's true operational time zone."
Hosted within these repositories are ZIP archives that, among other files, contain two specific components -
exe," and fails if the DLL is executed on its own inside a sandboxed environment.
Source link