A long-running Traffic Distribution System (TDS) known as Help TDS to a Russian-language affiliate program called Hotejka, which appears to be a rebrand of a traffic monetization operation dubbed ROI777.
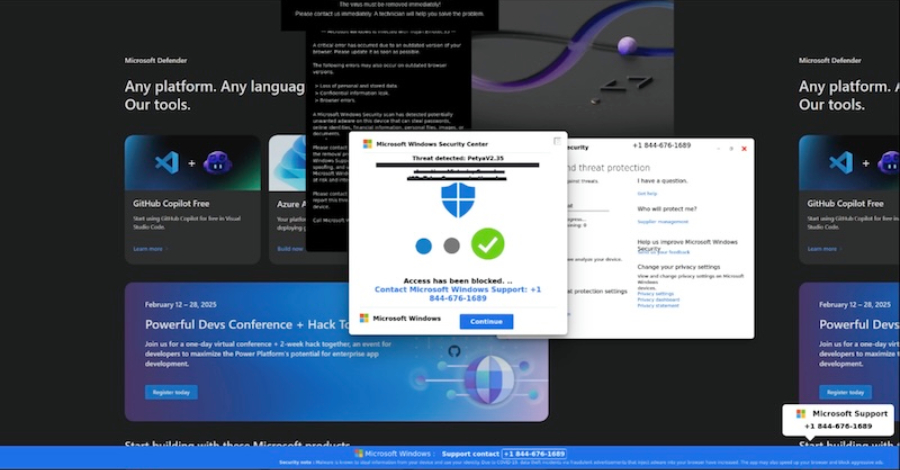
Help TDS is assessed to be active since at least 2017, offering PHP code templates to partners and affiliates that are installed into compromised websites with an aim to direct unsuspecting users to tech support scams. These scams make use of full-screen browser manipulation and exit prevention techniques to serve bogus Microsoft Windows security alert screens instructing victims to contact a Windows Support number to address the problem.
"Help TDS delivers tech support scams (TSSs) that direct users to call centers, where social engineering is used to convince them to install remote desktop tools," Infoblox said in a report shared with The Hacker News. "It's not simple credit card fraud: it's remote access, living-off-the-land malware operations. Once in, the threat actor can exploit the victim time and again."
Help TDS's evolution was documented by GoDaddy in August 2025, highlighting the threat actor's use of a malicious WordPress plugin named "woocommerce_inputs" on thousands of websites to steal WordPress user credentials and facilitate the malicious redirections by fetching the URLs from its command-and-control (C2) servers. The plugin, or alternatively a custom HTML block, is injected into the sites by Hotejka's affiliates.
Historical tracking of malicious redirect chains has also uncovered that Help TDS has routinely handed off traffic directly to VexTrio Viper , a cybercrime operator that runs an affiliate program to enable scams, riskware, spyware, adware, and pornographic content.
Source link