Candiru, an Israeli maker of spyware sold to governments, infected devices at the news network Al Jazeera through ordinary online ads, in attacks that needed no click or other action from the user, researchers at the Citizen Lab said Thursday.
The hidden attack code ran the moment an ad loaded on the screen, and in some cases the ad loaded out of sight, in the background.
The Citizen Lab, a research group at the University of Toronto, said this is the first public, technical confirmation that mercenary spyware, meaning hacking tools sold to governments, has reached real devices through targeted ads. The method had been described before from leaked company documents, but not shown in a live attack.
The researchers recovered the spyware itself from one device, but not the exploit that breaks into the browser or app to install it. That first break-in step is described from how the attack was set up, not from captured code.
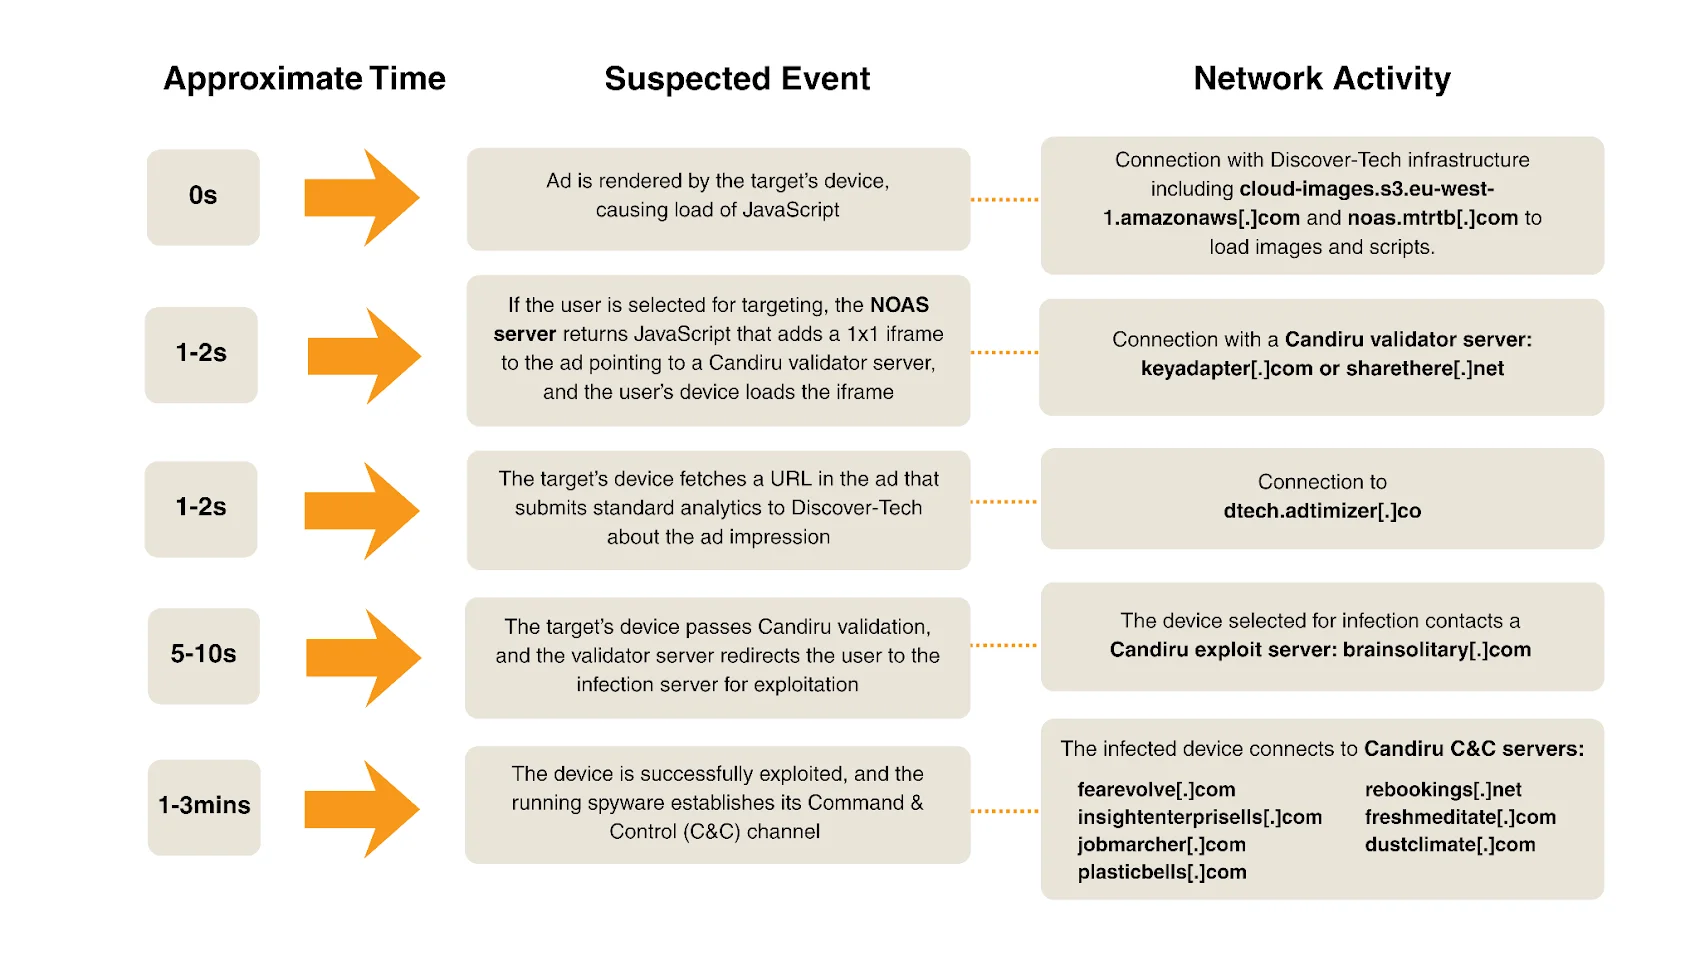
The ads were placed by Discover-Tech, an Israeli company that presents itself as a normal digital advertising firm. Each ad carried a small piece of code that, when the ad loaded, quietly sent the device's advertising ID and internet address back to a Discover-Tech server, the researchers found.
That server decided whether the device belonged to a target. If it did, the server sent back attack code for the browser or app to run. If it did not, the server sent nothing. Because the ad itself carried no attack code, the ad networks that delivered it had nothing harmful to detect.
Source link