A Chinese-speaking criminal pointed autonomous AI agents at company websites and let them break in with almost no help, and a security researcher watched it happen because the operators left their control panels open on the internet.
The agents tried more than 1,200 sites and reached websites belonging to more than 100 companies, including farm-equipment maker Deere, appliance company SharkNinja and engine maker Cummins, according to Reuters, which reviewed the attacker's own records to identify them. How much data, if any, was taken is not known.
The researcher, Snorre Fagerland of the security firm NorForge, found the operations by scanning the internet for exposed copies of Cairn, an open-source AI tool popular with hackers.
Beginning around October 2, he found about two dozen Cairn instances being used maliciously, which let him read the attackers' work in real time. He set out the findings on Monday, and Reuters, which saw the report before publication, named the victims from its own review of the attacker's activity.
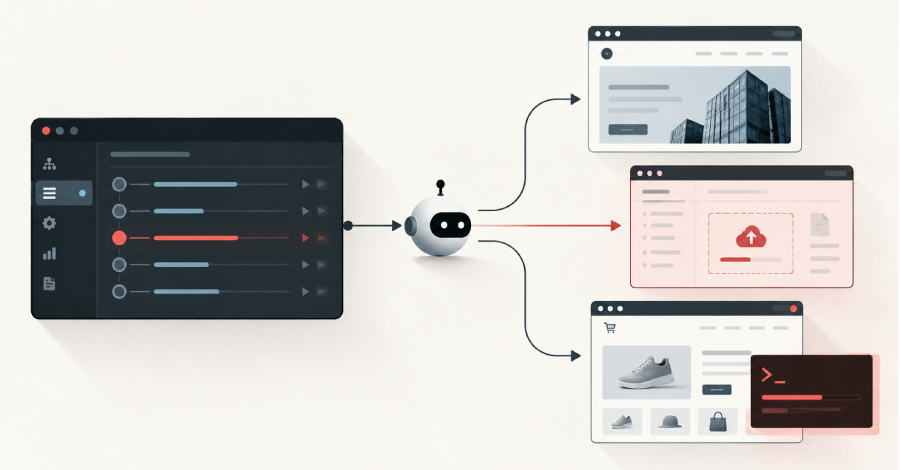
Cairn gives AI agents a starting point and a goal, then lets them work toward it step by step. The agents post what they find to a shared board, and the human operator can add hints along the way. It was built for authorized penetration testing and does other jobs too, but here it was pointed at online shops without permission.
Cairn's author, who posts as "le1xia0," told Reuters the tool was not designed for hacking attacks and that harmful use was not their intention.
Source link