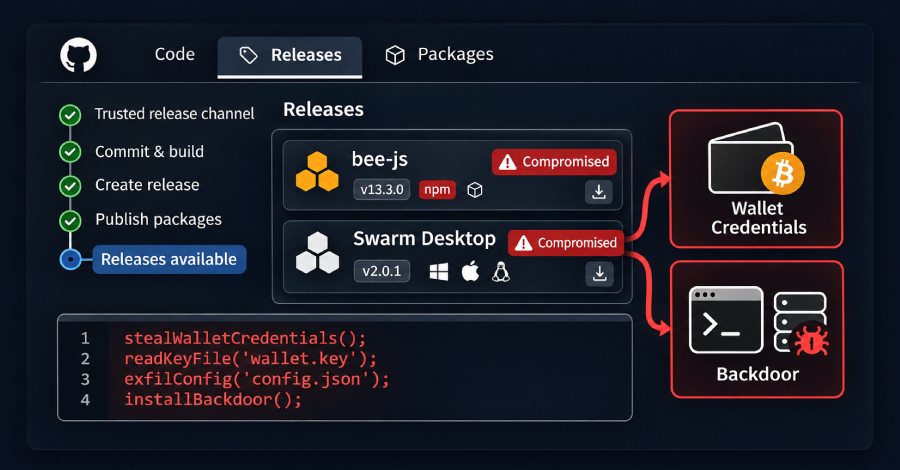
Attackers used the Ethersphere project's own release automation to publish malicious versions of two of its tools for the Swarm decentralized storage network: bee-js 13.3.0 and Swarm Desktop 0.56.2.
Both releases download and run code built to steal the wallet key that Swarm Desktop keeps for its node, along with the stored password that unlocks it. The code is also built to install a backdoor on Windows, macOS, and Linux machines.
The bee-js package is the JavaScript library behind Swarm Desktop and the swarm-cli command-line tool. Swarm Desktop runs a Swarm node on a user's own computer and saves the node's private keys there.
Both malicious releases have been taken down, and the project's maintainers released a clean Swarm Desktop update today. Neither step removes a backdoor already installed nor protects a key already sent. No theft of funds had been reported at the time of writing.
Swarm Desktop 0.56.2 appeared on GitHub at about 00:36 UTC today and was withdrawn about 8.5 hours later. The app's built-in updater could offer it to Windows x64 computers and Apple Silicon Macs within about 10 minutes, according to an incident analysis by Socket, a supply chain security firm. Intel Macs were never offered it, and Linux installs do not update automatically.
0, was the latest version on npm for about 75 minutes, from 00:09 to 01:25 UTC today. Its code runs as a postinstall script, which npm executes automatically during installation unless install scripts are disabled. A project did not need to import the library for the code to run.
Source link