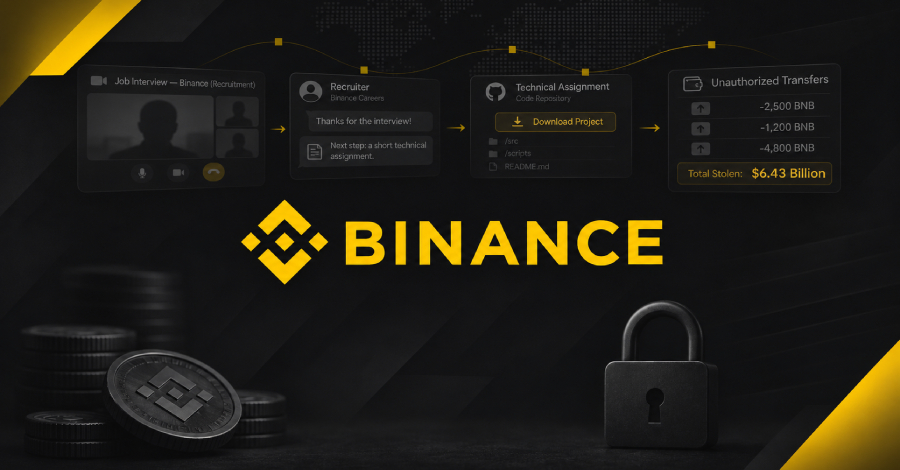
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a "sophisticated, multi-stage campaign" that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers.
"It was not a single isolated breach or a simple phishing incident," the company said. "The attackers combined a range of techniques, including social engineering by fake recruitment interviews, malicious software downloads, compromised internal AI tooling, endpoint compromise, and an advanced transaction-authorisation method."
The starting point has been traced back to a supply chain attack targeting one of its engineers from the Wallet DevOps team (named "Engineer A"), who downloaded a trojanized Homebrew installer to install a popular artificial intelligence (AI) tool after searching for it on a search engine. The incident occurred in June 2026.
Although Binance said it detected the attack and rotated all related credentials as a precautionary step, the company said information about "Engineer A's role and his related colleagues on our wallet infrastructure team was exposed to the hacker."
The second part of the attack occurred in September 2026, with the threat actor contacting another engineer (named "Engineer B") via a legitimate job-hunting platform by disguising themselves as a Project Director.
The Project Director persona arranged a first-round interview with a human resources (HR) representative, which was then followed by a second-round interview with an individual claiming to be the CEO of a non-existent company. Binance did not disclose details of the fake company.
Source link