GitHub has announced that it's introducing a new package firewall as a preview to block installation of suspicious npm packages during installation time.
"The firewall inspects both metadata requests and package downloads for signs of malicious activity, acting as an install-time policy gate," GitHub said.
The feature, which currently supports only npm packages, is available in public preview for all GitHub Enterprise Cloud customers, including data-resident GitHub Enterprise Cloud.
According to the Microsoft subsidiary, the firewall is placed between endpoints or internal registries and the upstream package repositories so as to deter malware attacks that compromise systems when packages are installed.
This behavior can expose users to severe security risks, especially when artificial intelligence (AI) agents and CI runners automatically install dependencies to complete a task or build without their explicit permission.
The idea is that endpoints like coding agents and CI/CD hosts use the firewall for their requests instead of directly pointing to the public package registries. The firewall then checks package downloads against policy controls such as minimum package age and malware advisories, and blocks downloads that do not meet those policies.
To use the firewall, administrators are required to configure policy controls, such as the ones listed below -
Block packages based on a cooldown period that prevents versions that are newer than the configured minimum age from being installed. The value can range from 1 to 365 days. The default value is 1 day. Users can disable it by setting it to 0.
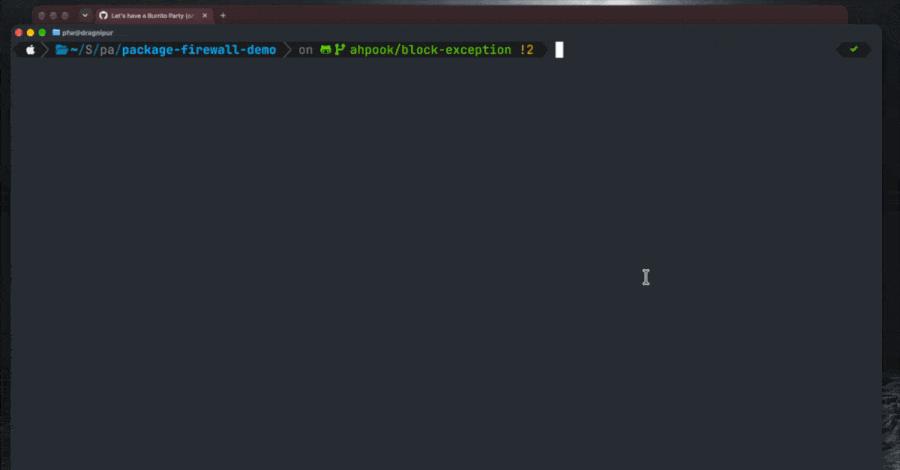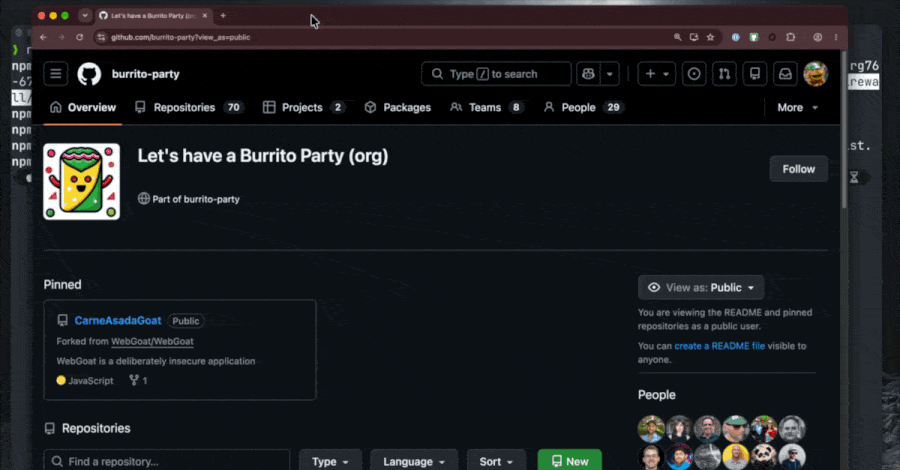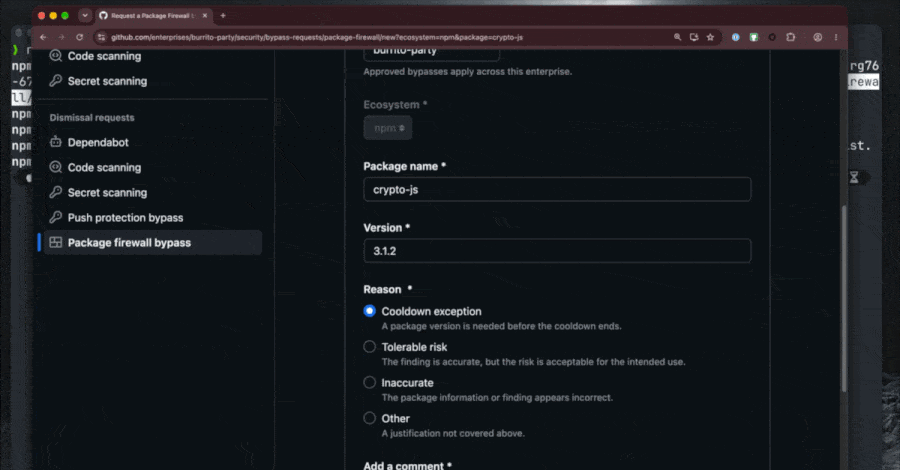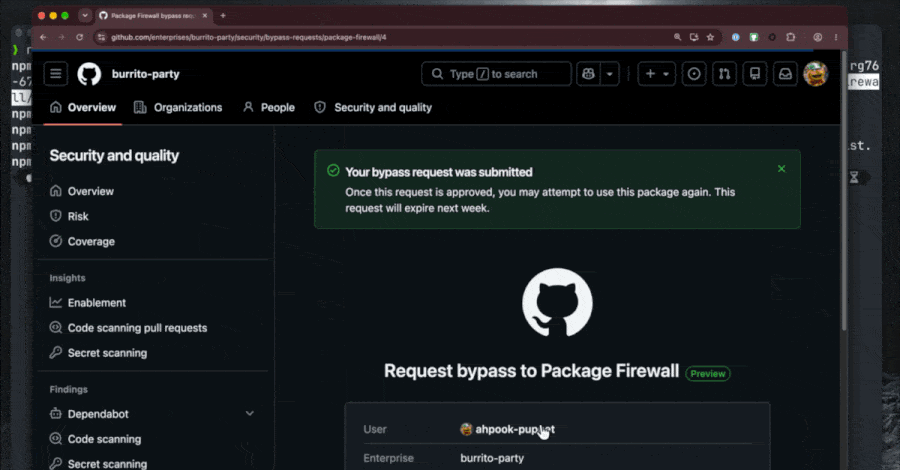
Users who need access to a package that gets blocked erroneously by the firewall can submit an exception request, which can then be approved by enterprise administrators and security managers.
Source link