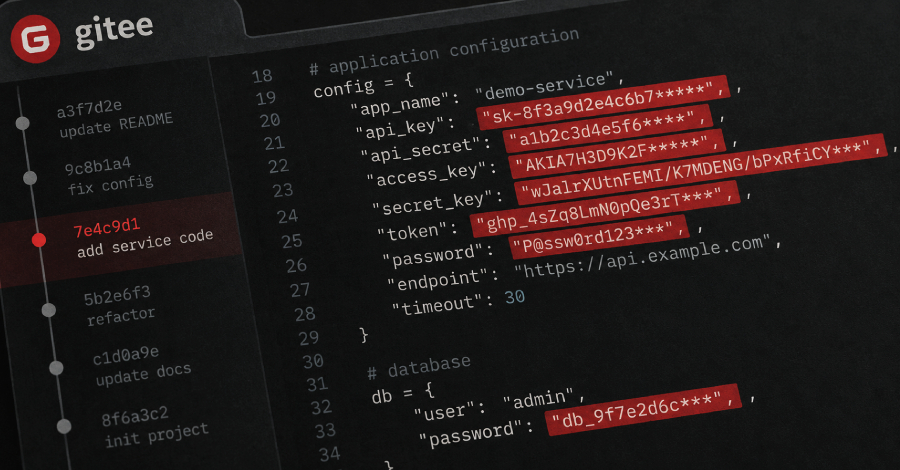
26,400 credentials that developers left in public code on Gitee, a Chinese code-hosting service, still worked when a researcher tested them. Anyone who copied one from that code could have used it.
Independent researcher Ben Zimmermann found them by scanning 7.25 million public Gitee repositories and reported the results on October 28. Most were keys for cloud and AI services, led by 9,473 Alibaba Cloud AccessKey pairs.
Zimmermann sent the vendors with the most exposed keys a list of their credentials, but he did not contact the developers who leaked them. When he published, he had not confirmed that any of the reported credentials had been revoked. So anyone who has pushed a key to a public Gitee repository cannot assume it has been revoked.
The scan ran for about a month, but Zimmermann did not provide the dates, so it is unclear how long ago the credentials were tested. He also did not say whether anyone else had used them.
He ran two secret scanners, TruffleHog and Kingfisher, over every repository. Both tried each credential against the service that issued it and kept only those that worked, he wrote.
The scanners read each repository's full commit history. A key that a developer later removed from the code could still be found and counted there.
The 26,400 figure counts each credential once, regardless of how many repositories it appeared in. By commit date, 12,242 of the credentials came from 2025, nearly half the total. Some dated to the late 2000s.
Source link