The French government has formally blamed Iran for launching cyberattacks that targeted thousands of internet-connected industrial refrigerated and freezer units across the country and broader Europe.
This is the latest in a string of destructive cyberattacks attributed to Iran this year, following a spate of hacks targeting U.S. water providers and other online intrusions that caused mass-disruption to U.S. medical device maker Stryker and others.
The U.S. government linked the attacks to pro-Iranian hacktivists who are working for Tehran, likely in response to the U.S./Israel-led war against Iran which killed its supreme leader in February.
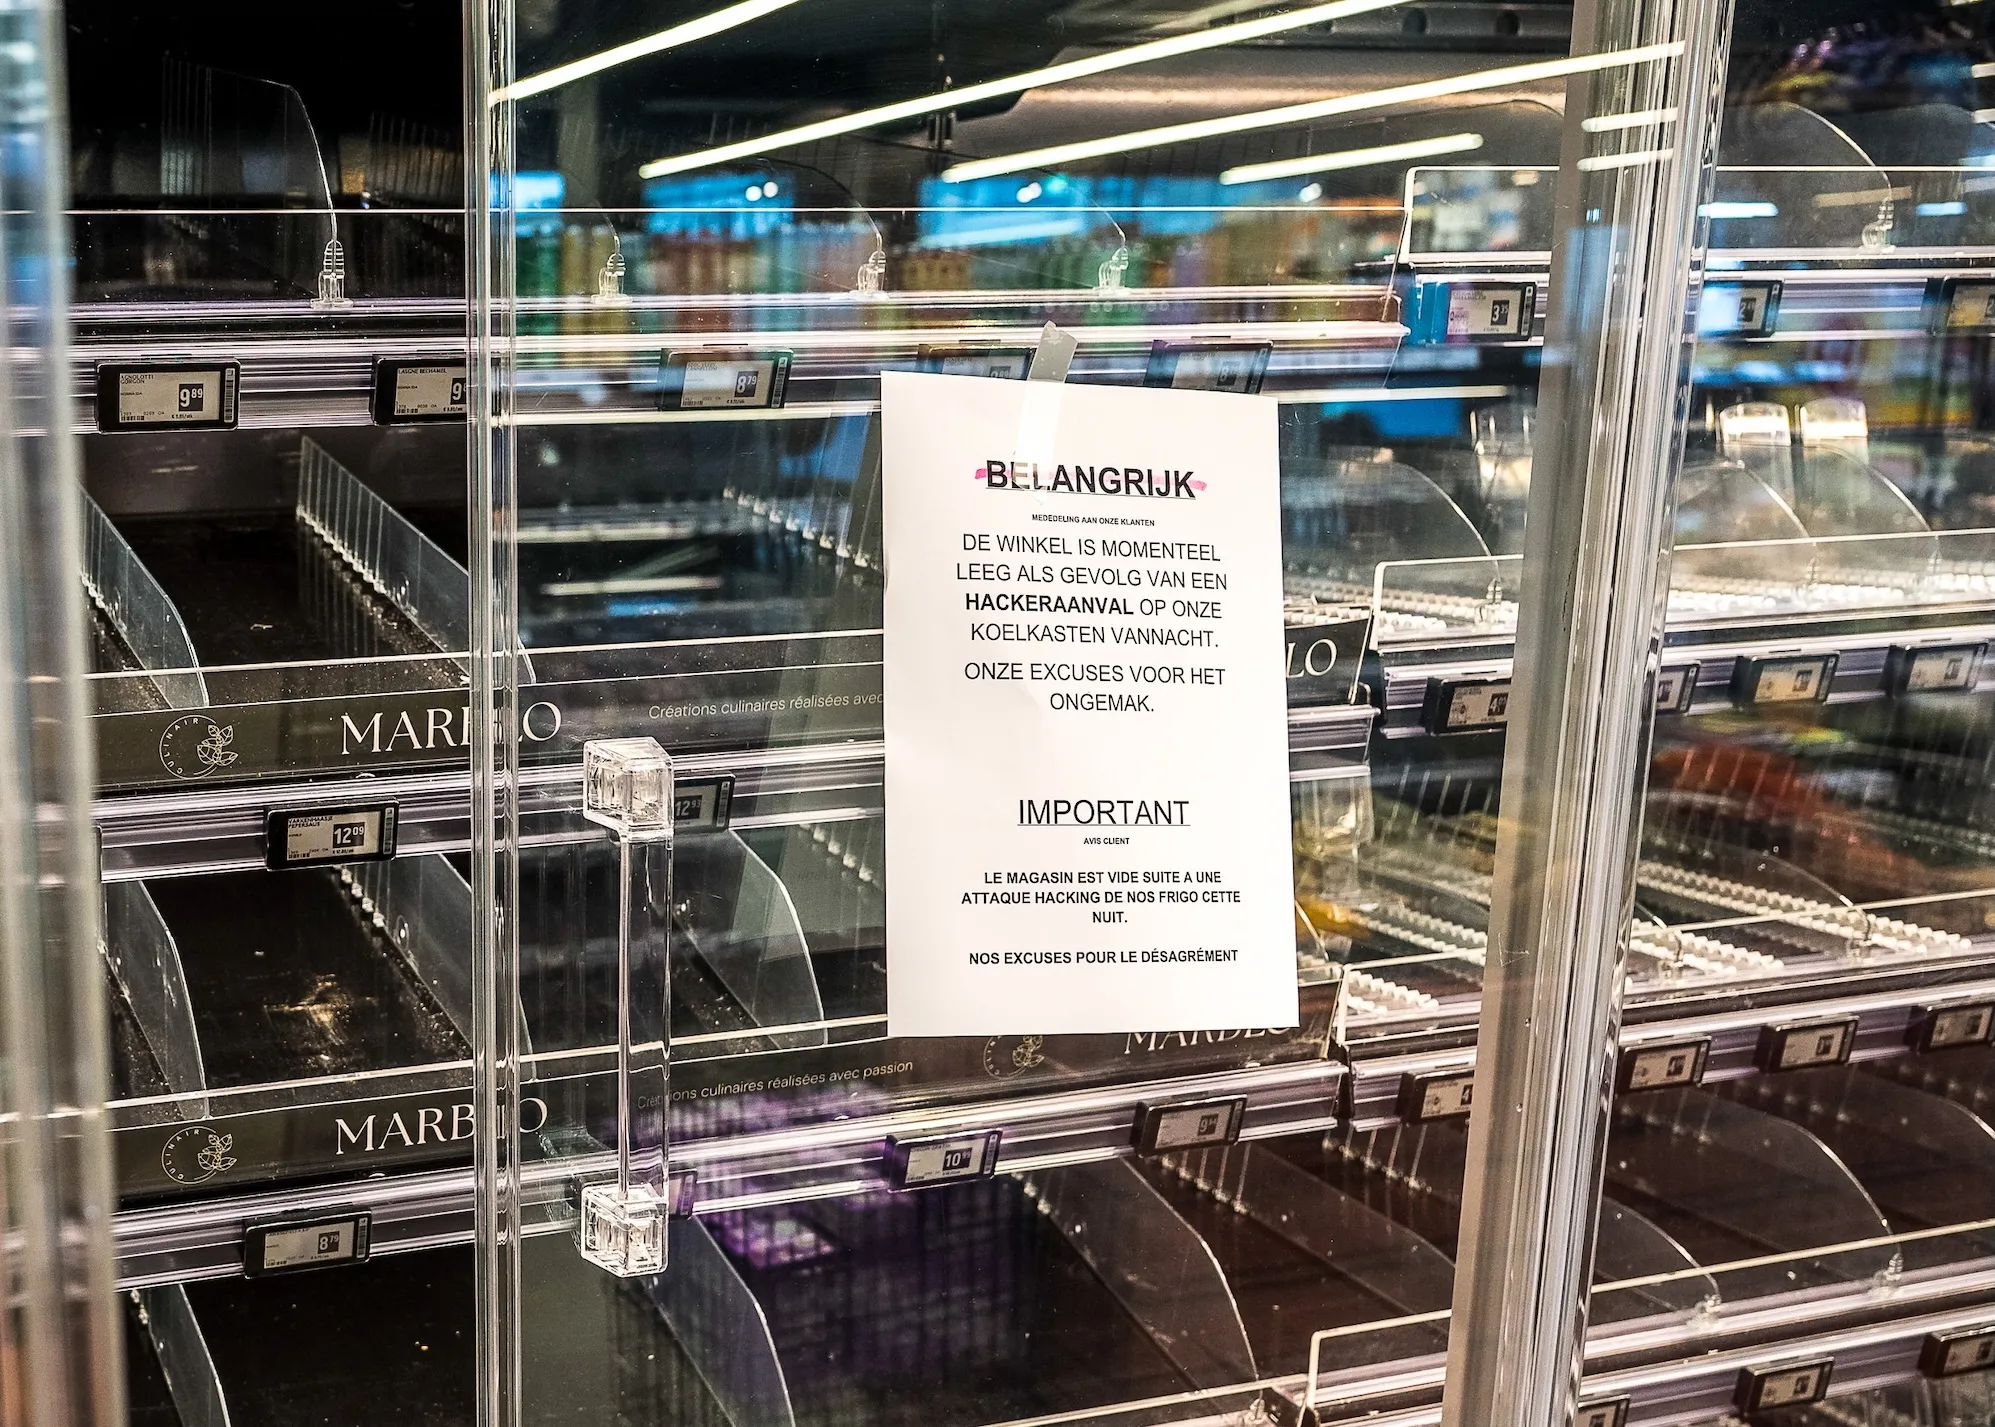
Two recent waves of cyberattacks throughout October and into November saw hackers remotely break into web-based controllers that manage fleets of industrial cold and chilling units at grocery stores and retail supermarkets, and raise the temperatures to spoil food and destroy goods. Medical blood banks were also hacked but the attacks were stopped before any blood was spoiled, according to the French Blood Establishment.
Security researchers have since warned that the web-based controllers are vulnerable to remote hacks, with some of the affected models made by Danish company Danfoss no longer receiving security fixes.
In a statement given to reporters in Paris on Monday, French foreign minister Jean-Noël Barrot said: “I am able to confirm that responsibility for this act lies with the Islamic Revolutionary Guard Corps,” referring to Iran’s military and hackers.
“This was an attack of unprecedented scale and aggression; it represents the first large-scale act of sabotage on our national territory and constitutes a major assault on the nation’s interests and the security of the French people,” said Barrot, adding that the hacks will “not go without consequences.”
Source link