Microsoft on Wednesday disclosed that a China state-aligned actor dubbed Storm-0940 was behind the recent supply chain compromise of the ConnectWise Cloud Backup application.
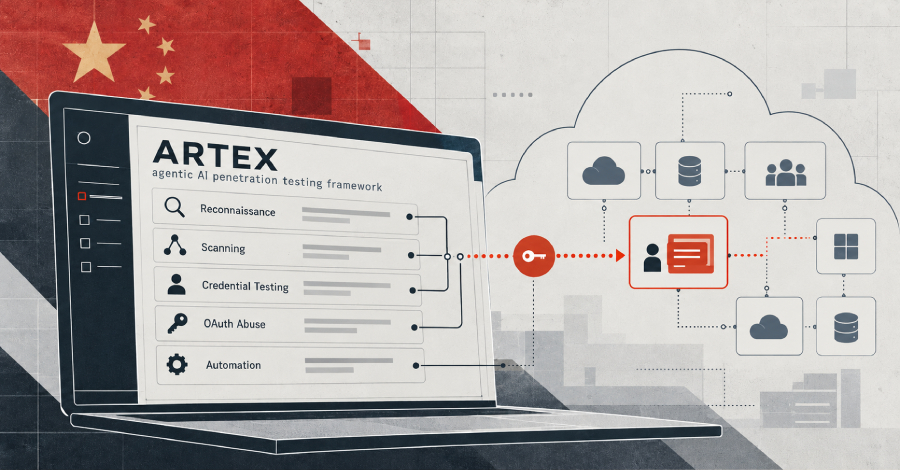
During the incident, Storm-0940 used ARTEX, a Go-based agentic AI penetration testing framework that was made closed-source in the wake of its abuse in cyber attacks targeting South Korean financial institutions, to speed up scanning and reconnaissance, password spraying, and OAuth application abuse at downstream victims.
The tech giant said the threat actor used the AI tool at "machine speed" to automate attacks targeting hundreds of organizations across the world spanning a broad range of sectors since September 2026. Targets include aerospace and defense, automotive, chemicals, energy, financial services, government, legal, manufacturing, media, military, semiconductor, software, technology, and think tanks and non-profits.
"Storm-0940's use of ARTEX accelerated the speed of compromised application abuse to authenticate to target environments through applications that had already been granted access, allowing the threat actor to operate without requiring an interactive user sign-in," Microsoft said.
"AI-accelerated follow-on activity included reconnaissance, application credential changes, and attempts to modify privileges that could enable expanded or persistent access."
Storm-0940 was first detailed by Microsoft in November 2024, revealing that the threat actor has been leveraging a botnet called Quad7 (aka CovertNetwork-1658) to conduct highly evasive password spray attacks. The threat actor is assessed to be active since at least 2021.
The adversary is also said to exploit internet-facing applications to gain initial access, followed by using compromised accounts to move through targeted environments.
Source link