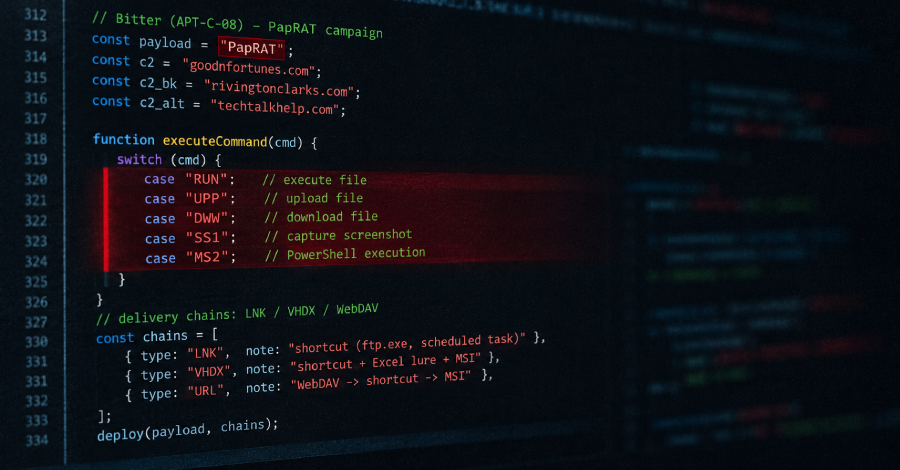
The South Asian cyber espionage group known as Bitter (aka APT-C-08, APT-Q-37, Hazy Tiger, Orange Yali, T-APT-17, and TA397) has been observed targeting South Asian organizations with a previously unreported remote access trojan called PapRAT.
"PapRAT has both C++ and Rust implementations," Fortinet FortiGuard Labs researcher Cara Lin said. "Its capabilities include command execution, file uploads and downloads, file deletion, directory and drive enumeration, and screenshot capture. The Rust variant adds PowerShell execution and other commands."
The campaign is notable for making use of three different infection chains -
The living-off-the-land (LotL) approach is designed to execute commands from a remote server ("goodnfortunes[.]com"), allowing it to collect directory and task lists, directory information from Desktop, Documents, and Downloads, installed antivirus product data, and mounted drives.
The harvested reconnaissance information is saved as "abc.pdf" and exfiltrated back to the C2 server via a curl command, after which the staged file is deleted from the host.
A second version of the script has been found to retrieve a file called "talk.log" from "techtalkhelp[.]com." The payload contains a Base64-encoded script to obtain additional instructions from the same server and execute them as PowerShell commands.
"This staging model gives the attacker operational flexibility, while the commands are updated server-side without pushing a new binary, avoiding PE drops and process injection that some security appliances could easily detect," Fortinet said.
The PapRAT malware delivered via the MSI installer in the second attack chain is designed for remote control. It supports eight commands -
A notable aspect of the third attack chain is that it combines the salient aspects of the first two sequences by using a script to download an MSI installer via curl.
Source link