
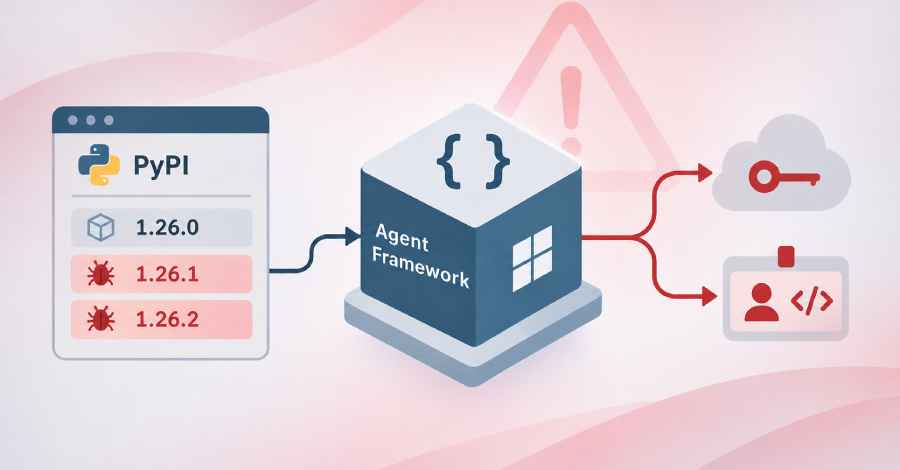
Threat actors have compromised Microsoft's agent-framework package to push a credential stealer, according to reports from Aikido, Chainguard, Endor Labs, OX Security, SafeDep, Socket, StepSecurity, and Google-owned Wiz.
The malicious versions, 1.26.1 and 1.26.2, were published 33 minutes apart on November 17, 2026, and are designed to run a credential stealer on every Python start. As of writing, both the release versions have been quarantined on the Python Package Index (PyPI) repository. It's unclear how the attacker managed to obtain publishing access.
Agent-framework is the meta-package for Microsoft Agent Framework, an open-source framework for building and orchestrating artificial intelligence (AI) agents using Python.
"Both versions install Python startup hooks that silently collect credentials, environment data, and cloud identity tokens, then exfiltrate them to a webhook[.]site endpoint," Socket said in a report.
Once either of the versions is installed, the package drops a .pth file in the site-packages root directory, which then gets executed automatically on every interpreter start, causing the credential stealer to run whenever Python is started in an environment, even if the package is not explicitly imported.
"Each wheel adds a .pth file to site-packages," Endor Labs said. "Python executes import lines in .pth files on every interpreter start, so the stealer runs on any Python launch in an affected environment, including pip itself, whether or not anything imports Agent Framework."
pth" file contains a single import statement referencing "agent_framework_meta," which then launches the stealer payload.
Source link





