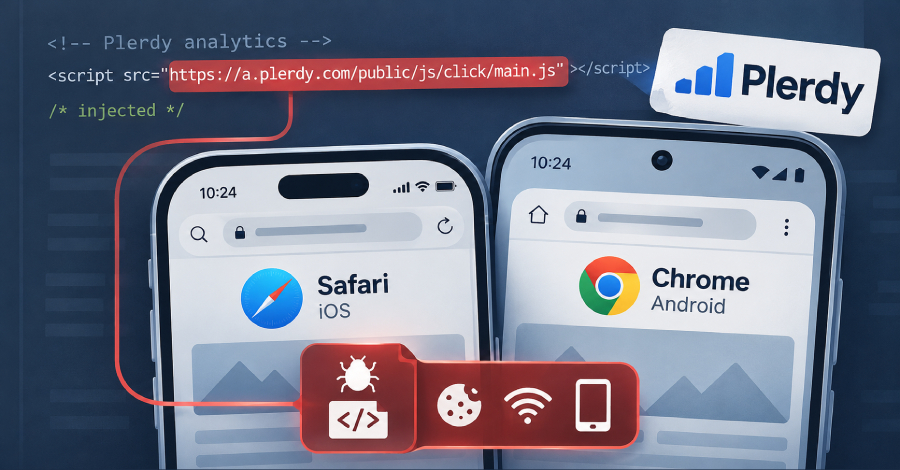
The Russia-linked threat actor known as APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker.
"The injected JavaScript code collects browser and device attributes," Sekoia researchers Amaury-Jacques Garçon and Félix Aime said in a technical report shared with The Hacker News. "Then, the delivery infrastructure delivers a platform-specific N-day exploit chain targeting either iOS or Android."
The end goal of the attacks is to serve payloads capable of stealing browser cookies, and in some cases, Wi-Fi passwords or full mobile device data. The activity, codenamed Poisoned Source, was discovered by the French cybersecurity company in mid-October 2026.
A defining aspect of the campaign is the use of three infection vectors -
Some of the compromised websites include a major industry trade association representing U.S. companies operating in the chemical industry, a far-right European political party, and a Bulgarian military-related website. It's suspected that the watering hole campaign may have been designed to target specific individuals rather than a broad effort.
"It remains unclear whether the attackers intended to target visitors to specific websites or sought to compromise as many unpatched mobile devices as possible, indiscriminately exfiltrating data before selectively identifying and exploiting information of interest," Sekoia said.
"However, several of these sites are likely to attract high-value or strategically important visitors in the context of the Russia-Ukraine war.
Source link