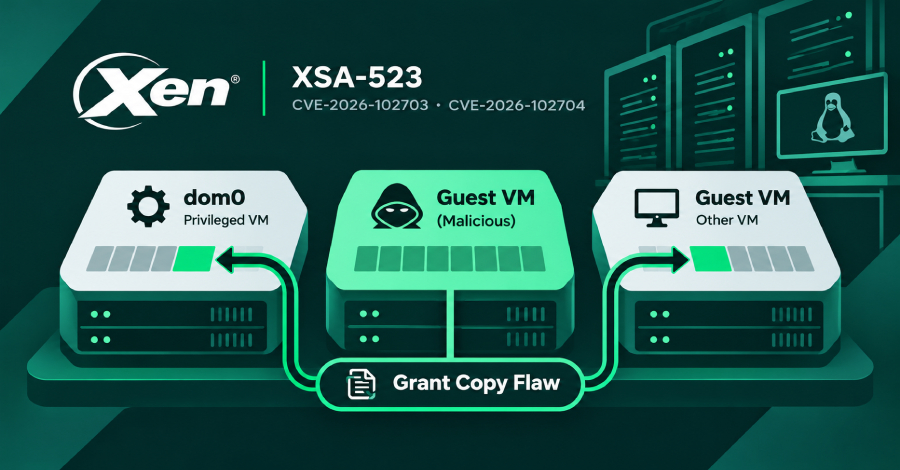
Two flaws in the Xen hypervisor allow a malicious guest virtual machine (VM) to read and write the memory of other VMs on the same host, including dom0.
Dom0 is the VM that, by default, has full permissions and manages the others. Patches are out, and there is no known mitigation, the Xen Project said in an advisory on November 3.
All Xen versions from 4.6 onward are vulnerable, while 4.5 and earlier are not. The flaws are tracked as CVE-2026-102703 and CVE-2026-102704, under Xen advisory XSA-523.
The Xen Project credited AI company Anthropic with finding the flaws using its Claude model. Stephan Lipp of Ada Logics then validated the finding, and the CodeAnt AI Security Research Team later independently reported the same issue.
The flaws are in grant copy, the operation Xen uses to copy data between VMs. Each VM tells Xen which of its memory pages other VMs may use, and Xen checks those permissions.
To save time on a batch of copies within the same memory page, Xen reuses checks it has already made. In some cases, it did not check again when it should have. That mistake is what lets a malicious guest read and write memory it does not own.
XCP-ng, an open-source virtualization platform built around Xen, said in its update notes that "a single compromised guest can break out of its isolation and take over the whole host."
Xen's advisory does not mention any attacks that exploit the flaws or specify what access within the VM an attacker needs.
Source link