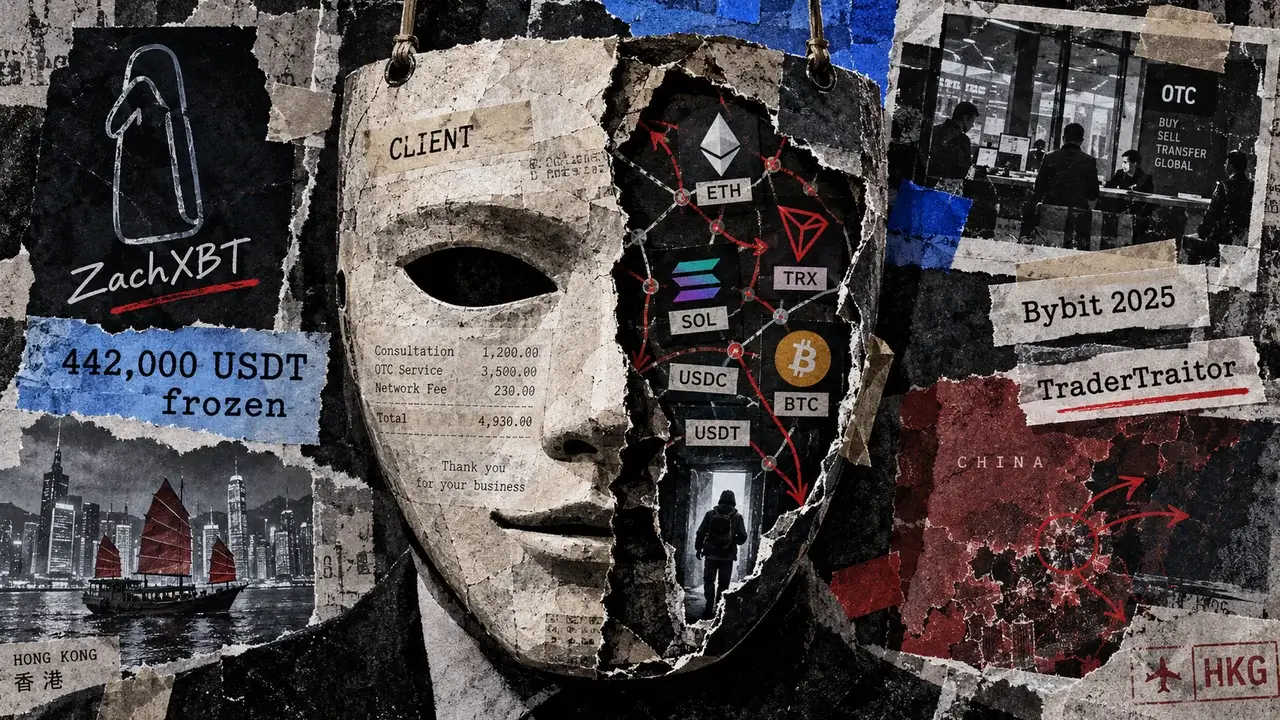
Blockchain investigator ZachXBT said he infiltrated a Chinese laundering syndicate by posing as a cryptocurrency client and funding repeated stablecoin trades.
In an Oct. 5 disclosure, he alleges the network laundered more than $1 billion across exploits for Lazarus Group.
He said he fronted 349,700 USDC to build a relationship with a contact using the alias Jimmy Green. According to his account, the repeated exchanges led to private conversations about moving funds stolen from Bybit in 2025.
He reported tracing a cluster involving more than $12 million in Bybit funds and a later 442,000 USDT freeze by Tether.
ZachXBT said the investigation began after the February 2025 Bybit exploit, when he noticed at least 15 accounts asking for help with orders he linked to stolen funds in public Telegram and Discord groups.
He contacted several of those accounts. One was Jimmy Green, the Telegram alias of the person with whom he subsequently exchanged funds.
On March 6, 2025, ZachXBT said he funded a new Ethereum address with 349,700 USDC in preparation for transactions with the contact. The arrangement involved sending his USDC on Ethereum in exchange for the contact's USDT on Tron. He then completed additional transactions to build trust.
As he built trust through repeat exchanges, ZachXBT said the contact began discussing movements of Bybit funds for North Korea before they occurred. The conversations also included details about operations in Hong Kong and mainland China.
In one example, he said the contact told him funds would move to Solana, and the movement happened the following day.
Source link