Keystone says it will destroy almost 19,000 unshipped hardware wallets after an attacker obtained the key it uses to verify its devices.
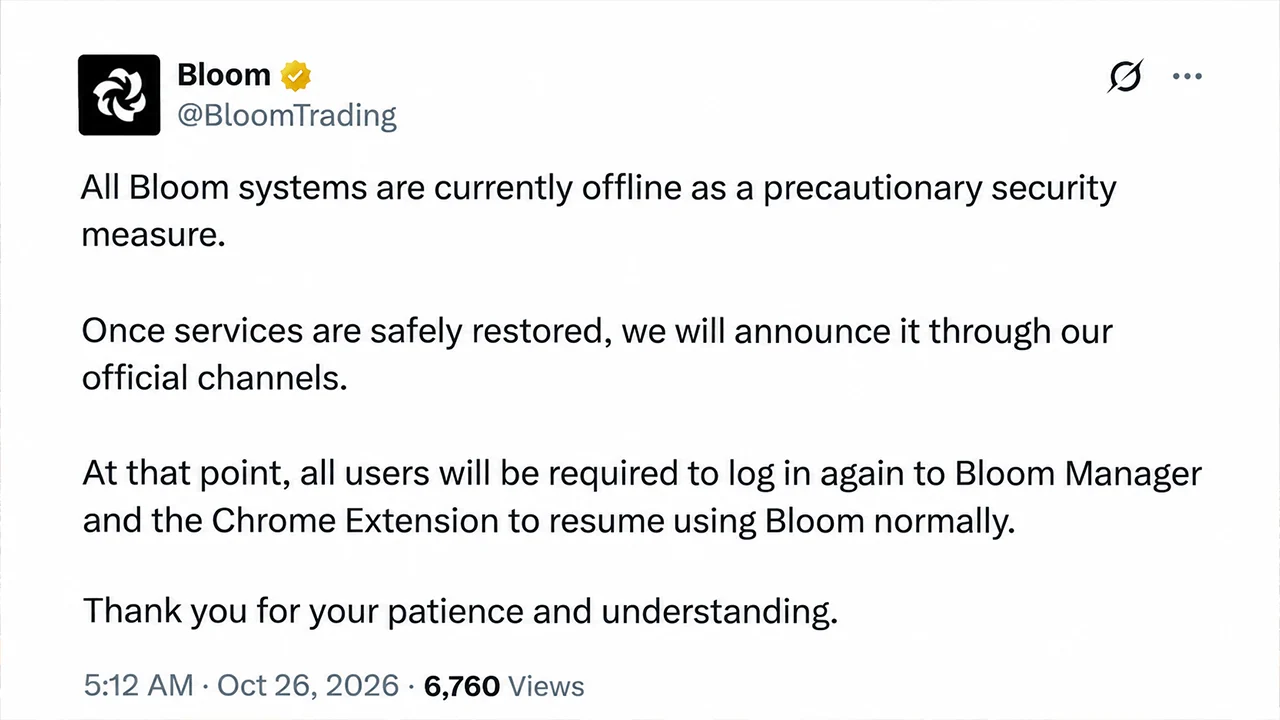
First, Keystone took to X on Saturday to confirm a suspected breach of customer shipping information, including “names, contact details, shipping addresses, and order details (items and prices).”
The confirmation came around 18 hours after a customer reported a “social engineering” call in which Keystone order information was used.
While sensitive payment information and wallet keys were not involved, the firm did warn against scammers impersonating its staff and “offering refunds, replacement devices, or ‘fixes’ for your order or address.”
We owe you an apology.
On October 20, we detected unauthorized access to our official website. After verifying API activity with Shopify, we confirmed on October 23 that a third party obtained customer shipping information. You trusted us with those details, and we're sorry we…
The company had previously promised that “180 days after your order, your shipping data is permanently deleted,” but the user that initially flagged the potential data breach claims that their device was purchased in 2024.
A later update put the total number of affected records at almost 26,000, limited to purchases made via Shopify on its official site (plus a further 13,000 incomplete purchase records of partial order information).
It also states that another 25,000 records had already been “permanently erased… in accordance with our data retention policy.” However, it concedes that its automated data deletion tool “did not operate reliably… resulting in certain personal information being retained beyond the permitted period.”
Source link