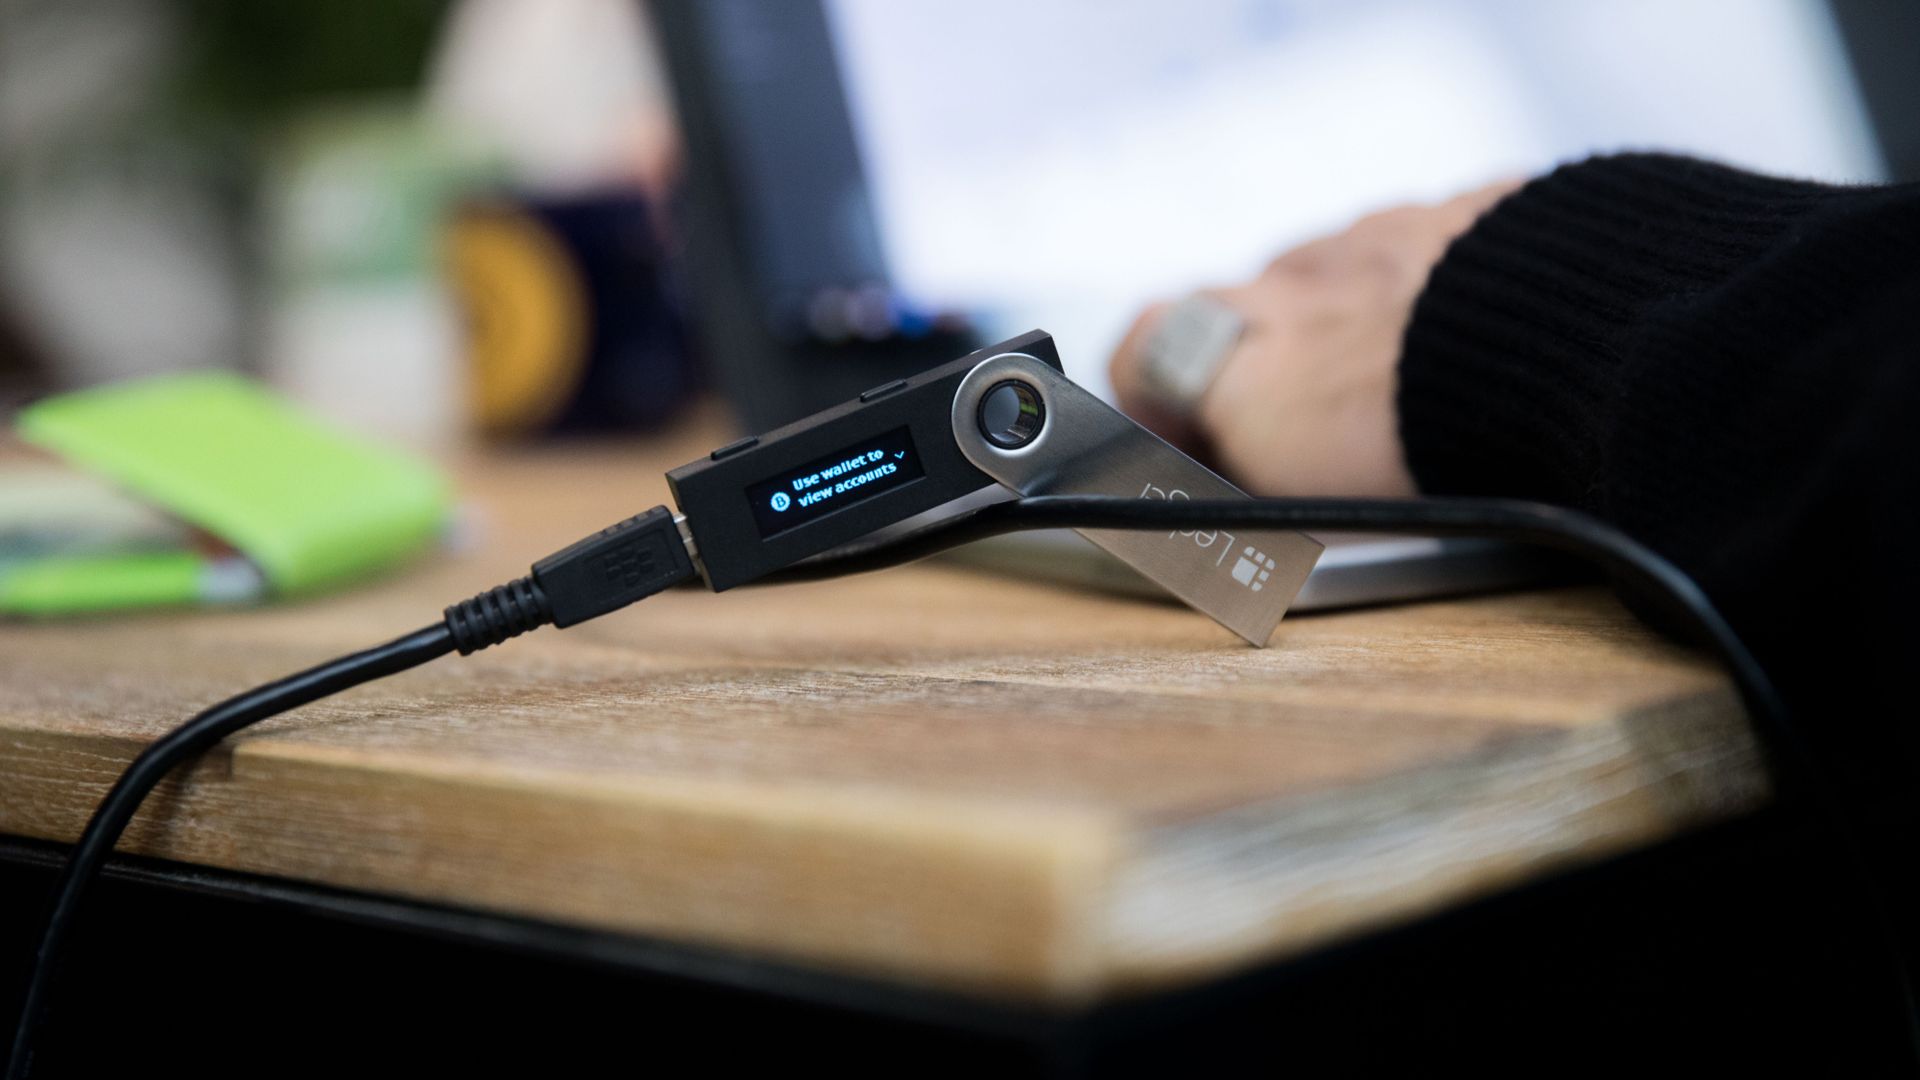
Cryptocurrency enthusiasts are often advised to acquire a hardware wallet like one of the Ledger models, theoretically adding the ultimate layer of security. And yet not even that approach is 100% safe, as a currently unfolding investigation revealed that Ledger resellers in Southeast Asia and Europe are carrying hacked wallets laden with eSIM and LTE modules for exfiltration of recovery phrases. At least $93 million (and going) has already reportedly been siphoned off users' balances. Hardware sold directly by Ledger is so far unaffected.
The first booby-trapped wallet originated from reseller Cryptobilis, which has currently ceased all sales of hardware wallets of all brands. The offending unit came from a store in Malaysia, though Cryptobilis also sells in Indonesia and the Philippines. Researcher Mark Karpelès has been looking into hacked wallets for a while now, and one of them came via Amazon Japan, bought from a Chinese seller and shipped from Malaysia. Cryptobilis also sells other brands of wallets such as Trezor, Coolwallet, and Tangem, though so far there is no news of contamination beyond Ledger.
JUST IN: UP CLOSE VIDEO SHOWS HOW HACKERS STOLE OVER $80,000,000 SILENTLY CORRUPTING LEDGER #BITCOIN WALLETSA SCAM SHOP IN MALAYSIA WAS LISTED AS AN "OFFICIAL AUTHORIZED RESELLER FOR YEARS"BEHIND THE SCENES, CRIMINALS WERE INSERTING MICROSCOPIC SPY CHIPS ON EVERY WALLETTHEY REPACKAGED THE DEVICE AND SHIPPED IT TO UNSUSPECTING VICTIMSALL THE WHILE IT WAS SILENTLY CAPTURING THEIR PRIVATE KEYS THIS IS WILD ‼️October 11, 2026
Ledger recommends that users who bought wallets from Cryptobilis in the past 90 days do not perform their initial setup, as that's where the private key exfiltration reportedly occurs.
Source link