

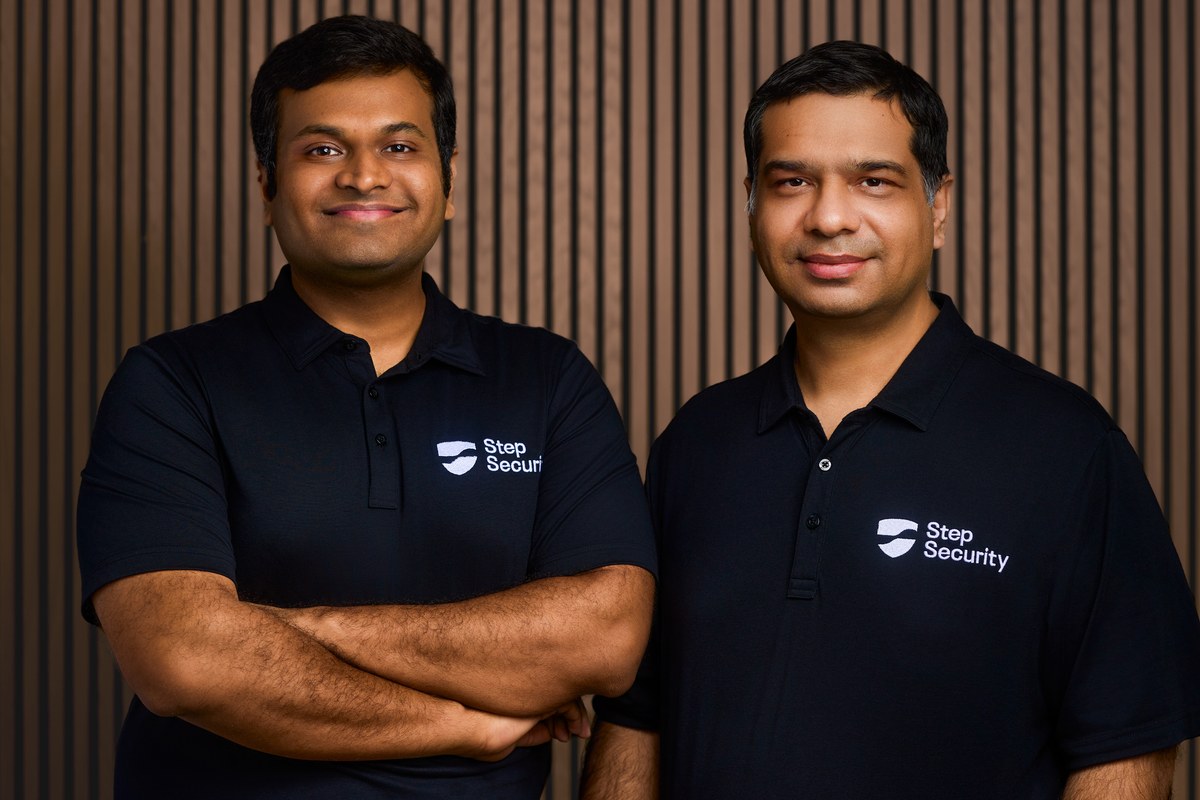
StepSecurity’s co-founders spent more than two decades combined at Microsoft. This week, as their startup announced a new round of funding, its researchers were also investigating a hacked Microsoft software package.
StepSecurity, a Seattle-area cybersecurity startup, raised a $20 million Series A round led by Elephant, with participation from existing investors Runtime Ventures, Inner Loop Capital and SaaS Ventures. The company has now raised $23 million, including a $3 million seed round in 2024. Axios Pro first reported the latest round.
The startup protects the systems used to build software: developers’ laptops, code repositories, package downloads and CI/CD pipelines, the automated systems that assemble and ship code.
The problem is that attackers increasingly slip malicious code into open-source software that developers download. That code can do damage as soon as it runs on a developer’s laptop or build system, stealing the passwords and keys that unlock other systems.
“A supply chain attack used to take a skilled team,” CEO Varun Sharma wrote in a blog post announcing the funding. “Now one person can vibe code it.”
Sharma spent about 15 years at Microsoft, where he led a team in Azure Security focused on making security easier for developers. CTO Ashish Kurmi spent nearly eight years at Microsoft before leading cloud security at Uber and infrastructure security at Plaid.
The two met at Microsoft and started StepSecurity in 2021, after working through the fallout from the SolarWinds and Codecov supply chain attacks at their respective employers.
Source link





