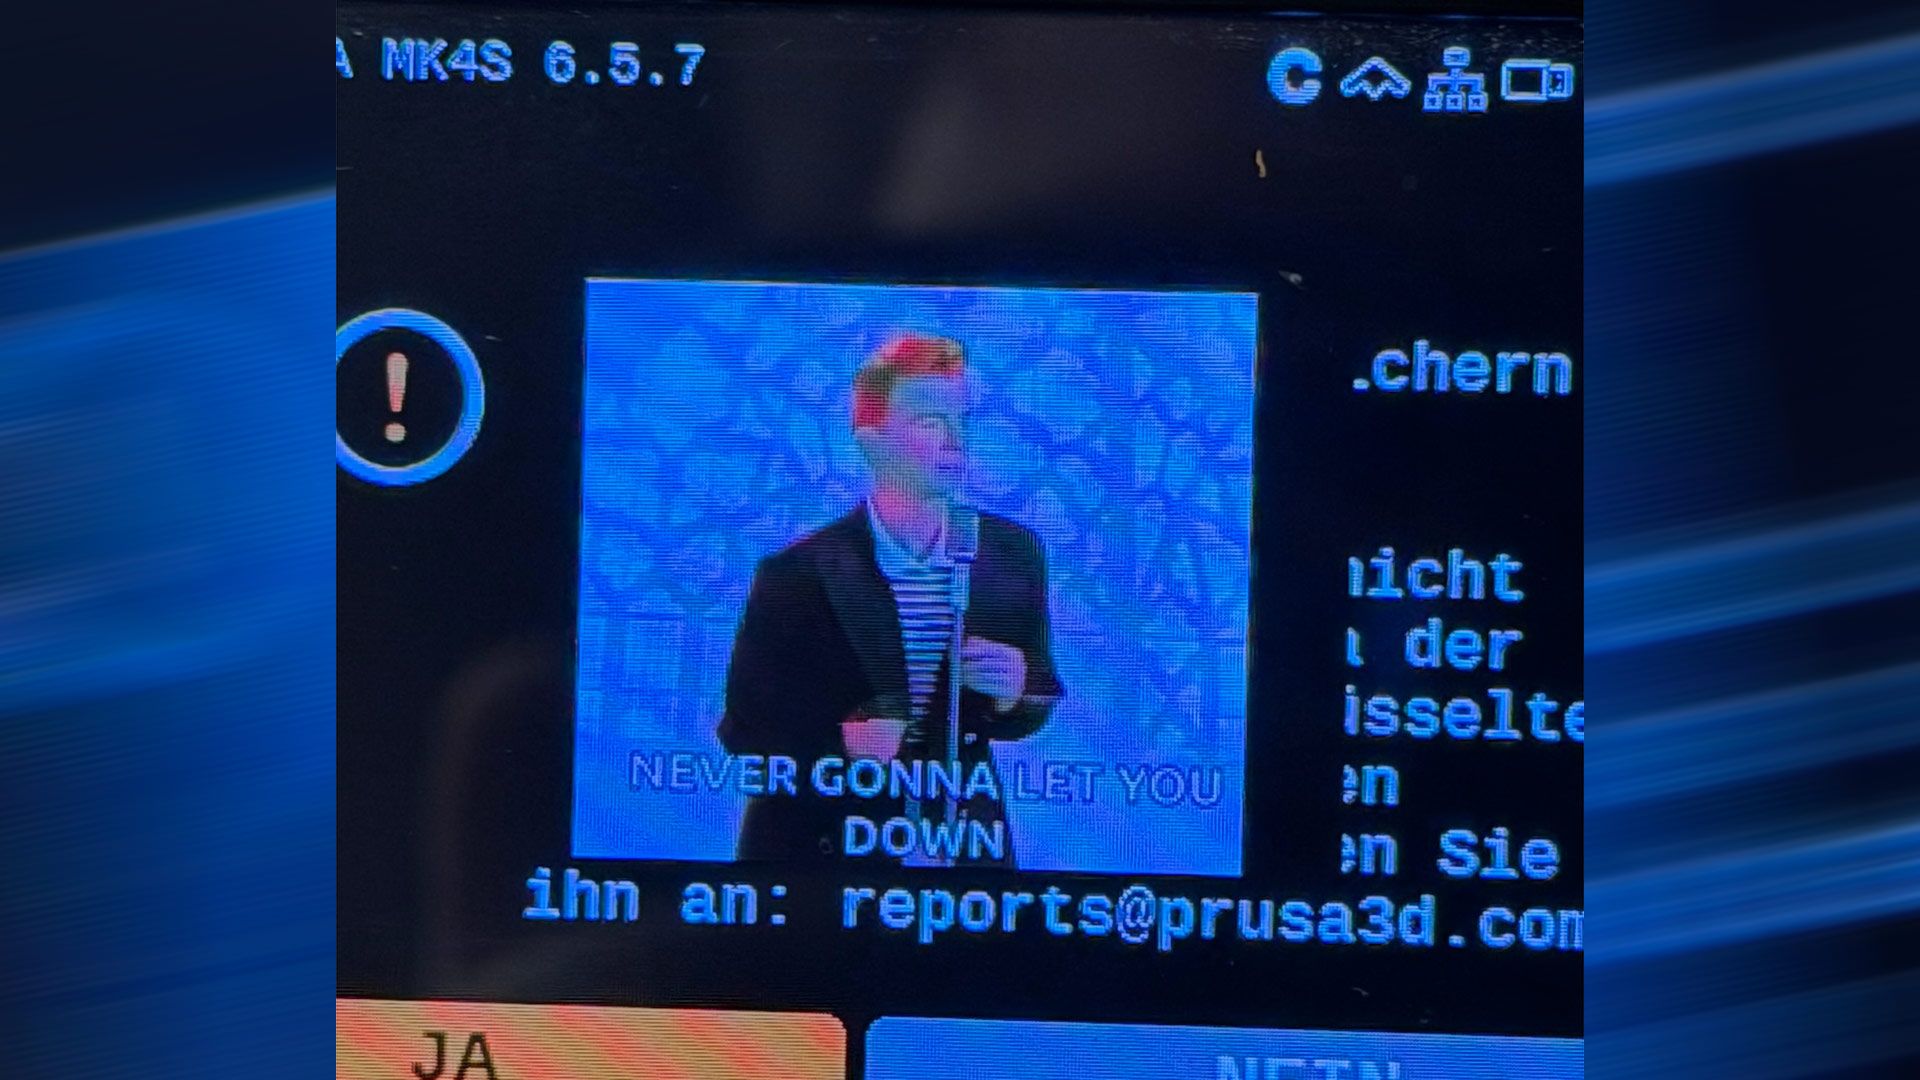
Software engineer Yannick Dixken spent a week attacking his Prusa MK4S 3D printer in the name of science. At the end of the relatively short but intense period, he produced a video demonstrating the ability to Rickroll the printer via remote code execution (RCE). Dixken shared the video and findings – charting “roughly 23 individual defects” with Prusa and published his amusing but detailed Never gonna print you up! blog in coordination with the 3D printer maker. Yes, all the vulnerabilities are now patched in the Buddy firmware versions >7.0.0.
Dixken is an experienced Freelance Cloud Architect, DevOps and Platform Engineer. Security research is more of a hobby, he notes in the blog post, but it is clearly a passion strong enough to spend a whole week probing the MK4S for vulnerabilities. The result is far more than the funny old Rickroll. The week of debugging, fuzzing and reverse engineering “armed with Opus 4.8 and a fuzzer” resulted in “14 findings, roughly 23 individual defects, and a chain that ends with the printer's main controller running code I sent it over the network,” noted Dixken. “Yup, fully fledged RCE.”
The headlining RCE scored 8.1 and is officially described as High Severity. This serious bug was in the cloud (or self-hosted) management platform called Prusa Connect. You can see proof-of-concept code Rickrolling the user in Dixken’s embedded video. He sent this video to Prusa.
The methods used to uncover these vulnerabilities are outlined in the source blog, if you’d like to know more.
Source link