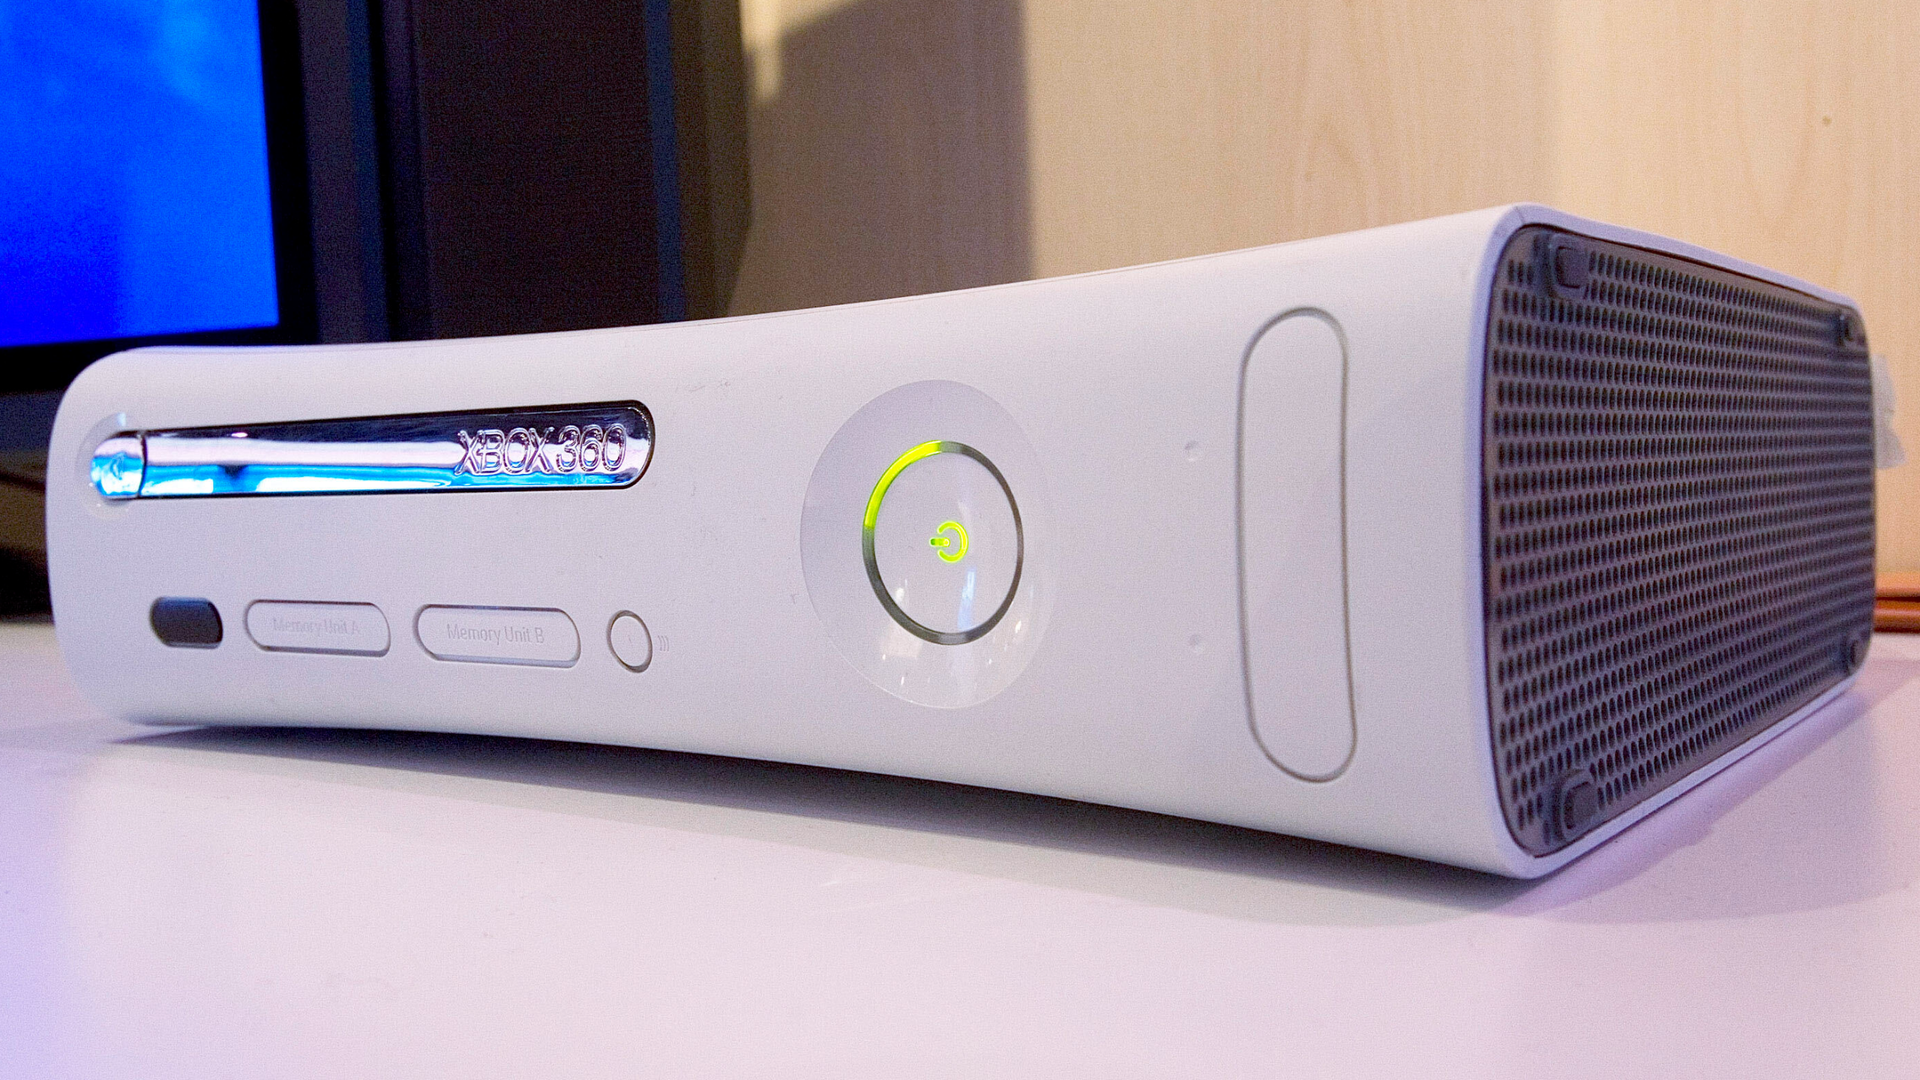
The Xbox 360 has been cracked open multiple times over the years, and almost every time Microsoft's updates plugged whichever hole let hackers through. The first method was modded DVD firmware in 2006, a hypervisor hack followed in 2007, and a wiring hack exposing JTAG debugging ports was revealed in 2009. The longest-lasting physical hack was 2011's CPU force-reset exploit. That maneuver needed specialized hardware along with a voltage-glitching chip, but an enterprising techie showed how it can be performed nowadays with the assistance of a Raspberry Pi Pico, costing all of $4 (or about 5€ / £5). The crack marks the culmination of a nine-year effort by the modder.
To get the elephant out of the room, yes, just last week the PeerPressure Xbox 360 persistent soft-mod was released. But we're here to talk signals and wires. The aforementioned reset exploit involves sending a teeny weeny tiny signal directly into the CPU's reset pin. You'd think this would do what it says on the label, but what happens instead is that the CPU executes the current instruction incorrectly.
Naturally, someone figured out how to leverage that to run any code on the CPU, thus completely bypassing Microsoft's impressive and frankly rather effective layers of cryptography within the console. Sending said signal for an effective hack, though, requires spectacularly precise timing with a resolution down to nanoseconds, and glitch-chips may even require several attempts to get a successful "latch."
Joshua Kennedy, a Scottish hacker, bought a Matrix Coolrunner Rev D modchip board back in 2017 to hack his console this way, but it required soldering wires, NAND, and programmers, and patience.
Source link