Bank Rakyat‘s websites were reportedly defaced in a suspected cyberattack late on 6 November, prompting the bank to temporarily restrict access to its corporate website.
Lowyat.NET reported that several of the bank’s webpages, including the iRakyat online banking login page, were defaced in an attack claimed by a threat actor using the name MARLANWG.
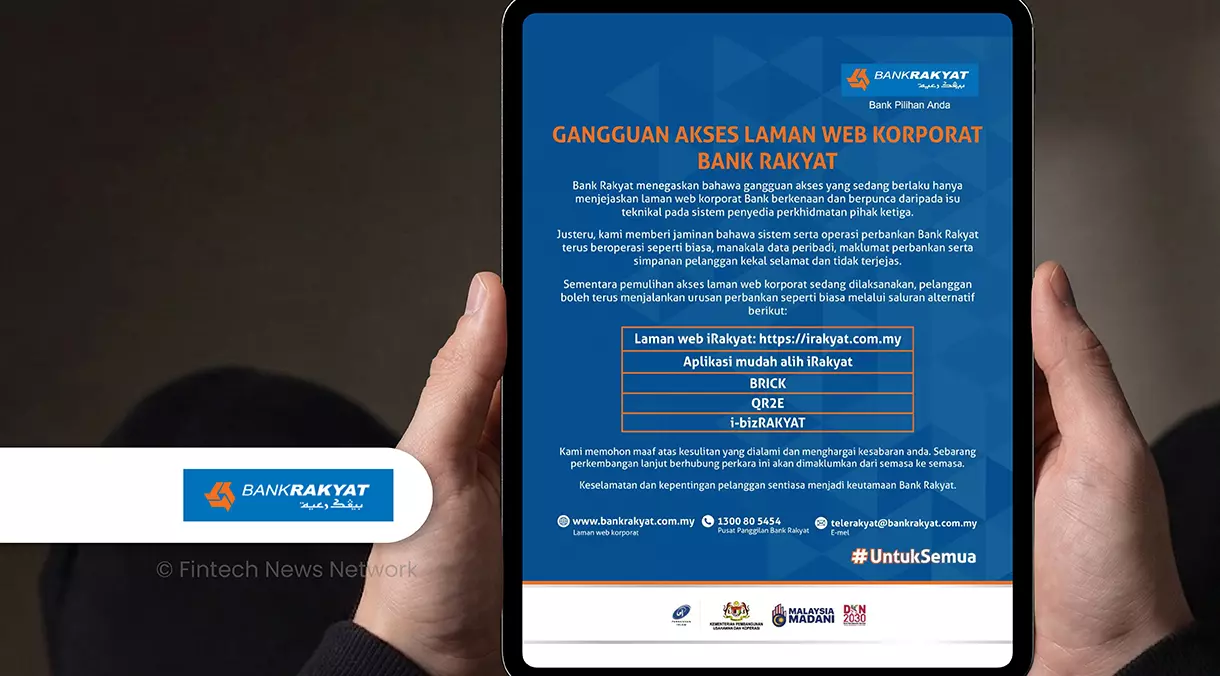
Bank Rakyat subsequently confirmed that its corporate website was temporarily inaccessible due to a technical issue involving a third-party service provider.
In a statement posted on 7 November, the bank said the disruption was limited to its corporate website and that customers’ personal data, banking information and savings remained safe.
The cooperative bank said its banking systems and operations continued to function normally.
Customers were advised to use alternative digital channels, including the iRakyat website and mobile app, BRICK, QR2E and the i-bizRAKYAT business banking portal while restoration work was underway.
Bank Rakyat’s statements did not explicitly confirm a cyberattack or mention the reported defacement.
The National Cyber Security Agency (NACSA), through its National Cyber Coordination and Command Centre, was monitoring developments involving several financial institutions, according to Lowyat.NET.
The incident comes after Bank Negara Malaysia (BNM) imposed a RM1 million penalty on Bank Rakyat on 20 January 2026 over cybersecurity and customer information protection breaches.
BNM linked the penalty to an earlier incident in which an external threat actor gained unauthorised access to the bank’s IT infrastructure.
It found that Bank Rakyat had failed to meet requirements under its Risk Management in Technology (RMiT) policy document.
Source link