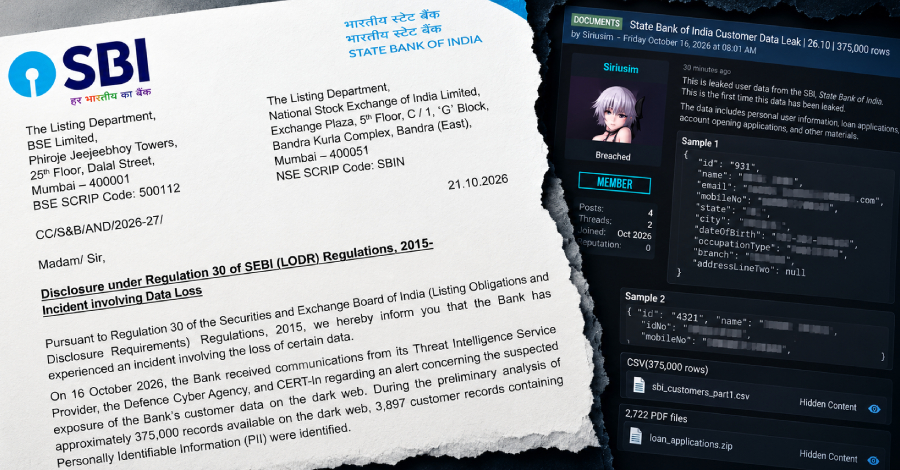
State Bank of India has identified 3,897 customer records containing personal information in a set of about 375,000 records available on the dark web, and it does not yet know where the data came from.
The state-owned bank, India's largest, said in a stock-exchange filing dated October 21 that it "has experienced an incident involving the loss of certain data." The count is preliminary, and the bank has yet to establish whether the data is authentic, how far the exposure goes and what risk it poses to customers.
The exposed information "reportedly included customers' registered mobile numbers, dates of birth, names, gender, email addresses, residential addresses, branch and CIF identifiers, lead IDs, and metadata associated with loan/lead records and other related files," in the filing's words. A CIF identifier is the customer information file number, the bank's internal ID for each customer.
The bank has not said whether the 3,897 records belong to 3,897 different people, or what the rest of the set contains. The 3,897 are roughly 1 in 100 of the records it examined.
Account numbers, balances, passwords, one-time passcodes, card details and government identity numbers such as PAN or Aadhaar are not among the categories the filing lists. The risk in the listed categories is impersonation: a caller or message that uses a customer's name, mobile number, date of birth, address, branch, and internal ID to appear to come from the bank.
The alert reached the bank on October 16 via its threat intelligence provider, CERT-In, India's national computer emergency response team, and the Defense Cyber Agency, the armed forces' cyber agency under the Ministry of Defense.
Source link