
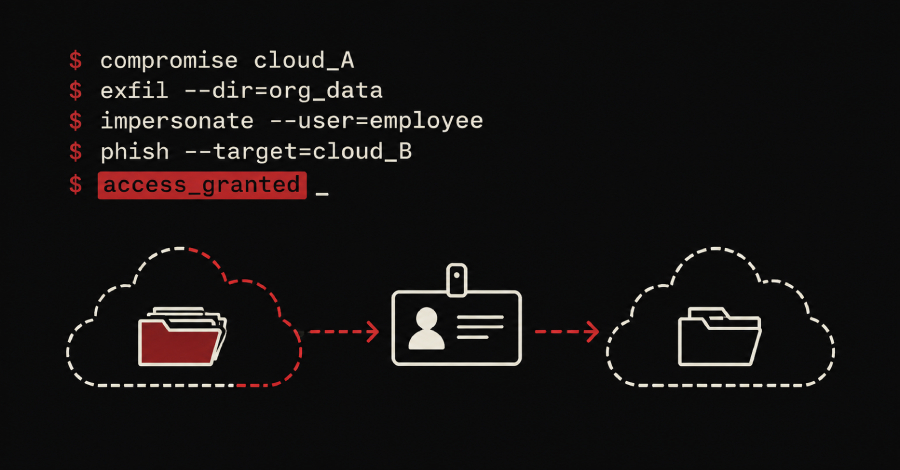
The Russia-linked cyber espionage group known as Cold Relic (formerly COLDRIVER and UNC4057) has been observed weaponizing a single cloud compromise into a launchpad for a series of linked intrusions resulting in third-party compromise.
Google's Mandiant and Threat Intelligence Group (GTIG) said it investigated a 2026 compromise at a U.S.-based organization in which the adversary leveraged data, the corporate staff directory, and identities harvested during a late-2025 compromise at a separate U.S.-based entity.
Cold Relic, also tracked as Callisto, Gossamer Bear, and Star Blizzard, has a track record of orchestrating sophisticated phishing and malware campaigns to gain access information that may be of strategic importance to the Russian government.
The access is abused to register rogue multi-factor authentication (MFA) devices, passkeys, and MFA backup codes to establish long-term persistence and then conduct aggressive data collection and exfiltration operations targeting email, chat, and cloud storage repositories. In addition, the compromised access is used to target the victim's social and professional networks.
Attacks mounted by the threat actor have successfully compromised high-value targets, including government officials, defense contractors, and non-governmental organizations (NGOs) across Europe and North America.
"Once Cold Relic compromises a target, it uses stolen emails and data to establish authentic pretexts and impersonate contacts when reaching out to subsequent targets," Google said.
-based organization in late 2025. Initial access to the network was achieved by means of a residential proxy network located in close geographical proximity to the victim.
Source link





